Written by: Jay You
Translated by: AididiaoJP, Foresight News
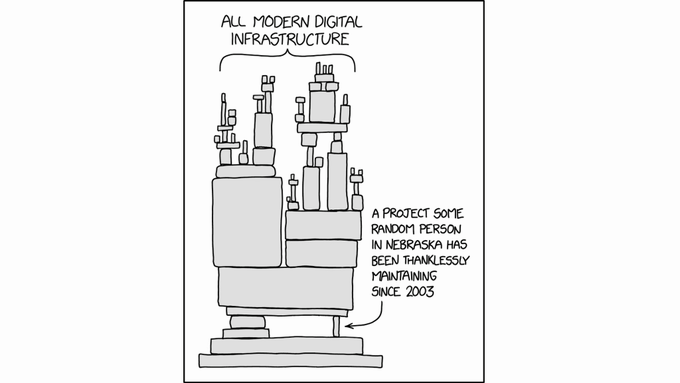
The original design of the internet was anti-fragile: when some nodes were taken down, the rest continued to operate as usual. But today's internet resembles a crumbling tower, piled high with various libraries, dependencies, and development environments, with a few key components pressed down at the bottom. There are few people maintaining it, and even fewer checking it.
In October 2026, a series of attacks exposed this fragility very clearly.
PHP revealed the “PHP2Shell” vulnerability, with over 5 million hosts facing the risk of remote takeover. The release process of LiteLLM was hijacked, resulting in a credential-stealing version being uploaded to PyPI. Railway had up to 100,000 workspace storage keys decrypted, with attackers searching for AI API keys. Fireworks AI was breached twice: the first time due to its own credential leak, and the second time when the cloud service provider was hacked. The certificate authority eMudhra issued a trusted signing key that was weak enough that one of them was the digit “4.” Binance's hot wallet was hacked for $6.3 billion, attributed by the FBI to North Korea.
These attacks illustrate how dangerous AI agents can be as attackers. Conversely, agents could also be a key part of the solution. They can accelerate the migration to more secure languages and formal verification, speed up the adoption of cryptographic products like zero-knowledge proofs and trusted execution environments, and potentially give rise to a "dual-lane" internet governed by identity and content authentication, allowing agents and humans to operate on separate paths.
As agents drive down the cost of writing software, the most valuable codebases will increasingly resemble living systems: cutting-edge models constantly perform penetration tests, with each iteration hardening the code, language, and toolchain, eliminating entire classes of defects. In this way, we can use agents to strengthen the internet into something anti-fragile—every time an agent goes live, the internet becomes stronger, not weaker.
1. The Triple Role of Agents: Weapons, Targets, Impersonators
Agents are changing the structure of the internet in three ways.
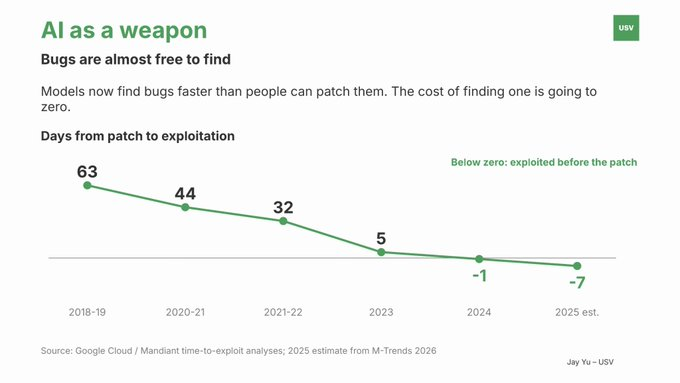
First, agents are weapons. The safety of legacy code largely stems from the high cost of exploiting vulnerabilities. Agents have driven this cost toward zero. PHP2Shell remained hidden in PHP for over a decade, yet Wiz's white hat team turned the vulnerability into an actionable attack tool in just a few hours using cutting-edge models. According to Wiz, AI has lowered the barriers to developing and modifying complex exploits, turning previously impractical vulnerabilities into feasible targets. Attackers are already leveraging this. In a spy case discovered by Anthropic, AI completed 80% to 90% of the operation. The October attacks represented a re-enactment of this same pattern on an internet scale: finding a weakness and quickly hitting millions of targets.
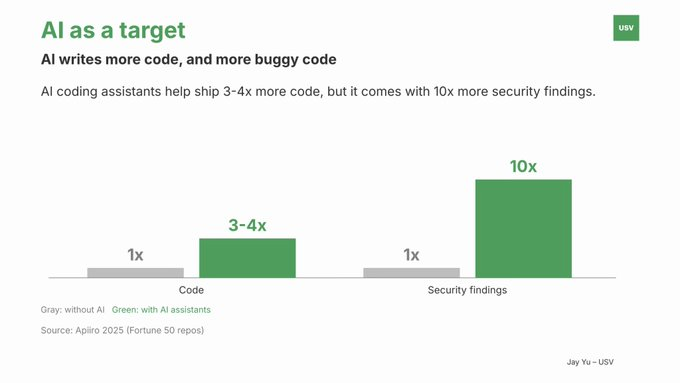
Second, agents are also targets. A significant amount of new code is written by these tools, making both the agents and the code they write susceptible to attacks. Consumer-grade agents like Muse and Instinct, as well as enterprise-grade agents like Sierra and Decagon, operate in the open tool landscape and face attacks such as prompt injection, which have become increasingly sophisticated in recent years. Agents can also introduce more bugs into the code. LiteLLM was hacked this time, possibly involving an AI agent inadvertently writing a GitHub token into the logs. Even if we let code-writing agents fix security issues, their implementations are often unreliable.
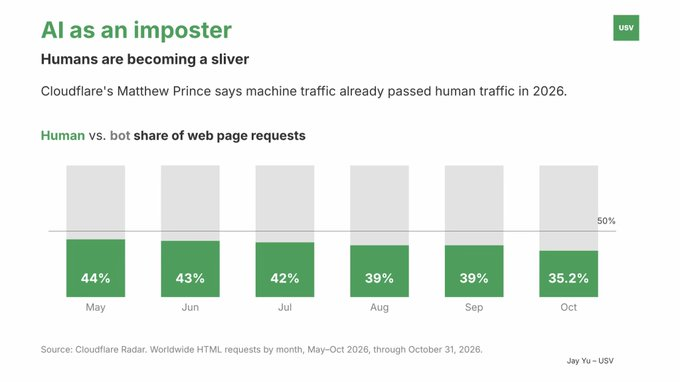
Third, agents can impersonate humans, challenging the existing traffic rules of the internet. Data from Cloudflare shows that by 2026, half of internet traffic will no longer come from humans. CEO Matthew Prince predicts that in five years, automated traffic will reach "1000 times human traffic." These agent activities are overwhelming websites designed for human browsing. In October, the Wikimedia Foundation reported millions of malicious OpenAI agent requests to access its website, potentially causing the Wikidata service outage. There was also a diner’s Instinct agent calling Resy hundreds of times an hour every day until the account was banned.
Some initiatives have already been launched to label and identify agent traffic, such as Meta and Sierra's Personal Agent Protocol, but these measures alone are not enough. Agents often have motives to hide their identities: many websites still treat non-human traffic as malicious, and self-reported agents can get banned mid-task, while those impersonating humans might slip through.
2. Three Responses: Observe, Execute, Prevent
The roles of “weapons, targets, impersonators” tell us where the threats come from, but they don’t tell us what to do about it. We can add another axis with three response methods: observe, to find vulnerabilities and monitor agent behaviors; execute, to patch more quickly and limit what agents can access; and prevent, to design systems so that entire classes of failures simply do not occur. The intersection of these two axes forms a map of today’s startups.
According to this map, most companies and visible capital are concentrated in the "observe" and "execute" layers. These two layers are easier to penetrate and integrate with existing software stacks. Major players are already present here: Socket raised $125 million, Braintrust completed an $80 million Series B, and Armadin raised $445 million.
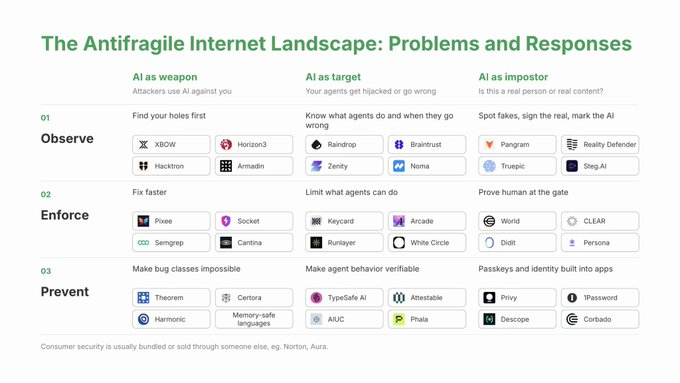
The winners in the observe and execute layers are likely to be those that capture the most agent logs. Whoever sees the most agent behaviors can write the best strategies; this is perhaps the closest thing to a network effect in this market. If detection capabilities improve with accumulated data, the advantage will shift to independent vendors—they can observe traffic from different clients and models, rather than just focusing on one laboratory.
But what is more worth watching for a long-term answer is how to write secure software that can prevent or eliminate entire classes of bugs. Prevention means designing software and agents so that failures of a certain type simply do not occur. History shows that such a transformation requires several conditions to align: a shock that makes the costs visible, a tool that easily integrates into workflows, and a force that pushes it to become the default standard.
Memory safety once accounted for nearly 70% of Microsoft CVEs. Rust emerged as a viable alternative and has increasingly been used in agent system programming, becoming one of the fastest-growing programming languages by percentage. HTTPS followed the same path: the Snowden incident was the shock, Let's Encrypt provided free, user-friendly tools, and Chrome marking HTTP as "not secure" was the push. Today, attacks from October have already constituted a significant shock. The tools might be formal verification toolchains, and the push might come from testing frameworks, regulations, or functional network effects.
Furthermore, as agents become the primary traffic on the internet, identity and security issues may converge. In the cloud era, Okta and Wiz are two companies solving essentially the same puzzle: who can access which cloud resources. Agents face similar resource authorization issues, especially when they use connectors like APIs and MCPs to access context repositories.
Agent identity has two paths: identity provenance and content verification. Both paths may be necessary. Identity provenance includes signature requests and identity protocols, such as PAP or A2A, to sign and verify the actor and content. But as mentioned earlier, agents often have incentives to hide their identities when completing tasks, and malicious actors are even less likely to comply with these standards. Content verification fills in the remaining part: using actual behaviors and output content to detect and make decision trees, allowing websites to judge who is human and who is a robot even if they cannot see badges.
3. What Comes Next
1. The Great Code Migration
Things may first get worse before getting better. There is a vast amount of legacy infrastructure around the world, much of it written in an era when the costs of discovering and exploiting vulnerabilities were very high. This assumption no longer holds true as agents push the cost of attacks toward zero. In the next one to two years, these attacks could prompt a "great code migration": shifting from insecure legacy codebases and languages to more modern, anti-fragile stacks.
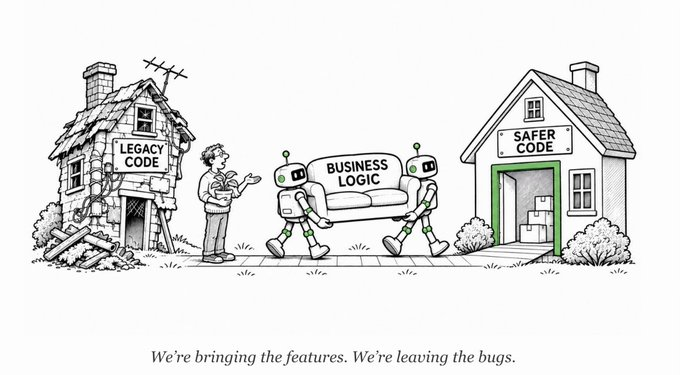
In the past, manually rewriting large legacy codebases into safer languages like TypeScript and Rust was an extremely difficult and costly endeavor. Agents have completely changed the equation. GitHub Copilot recently migrated 832,000 lines of runtime to Rust in three months, with almost just one engineer working on it. Without agents, this task would have required an entire team a couple of years. The widespread availability of newer, safer AI models will also accelerate: TypeSafe's Jev returns typed structured reasoning instead of unconstrained outputs, achieving close to 13% utilization in Vercel’s paid AI gateway team within just one day.
Today, a new stack of security tools is being rebuilt around agent programming: code reviews (Greptile), code and key scanning (Semgrep), malicious package dependency checks (Socket), agent runtime failure detection (Raindrop), production incident response (Resolve AI). New deployment layers are also forming beneath them: agent sandboxes (E2B, Daytona), authorization and tool layers (Composio, Nango, Arcade). Together, these could form an anti-fragile developer stack: every bug found in development, testing, or deployment can feedback into the next line of code.
As code migration becomes cheaper, formal verification may receive renewed attention at the compiler and toolchain levels. For instance, in a collaboration between Theorem and Anthropic, Claude proved security properties for over 100 open-source libraries.
However, code migration also has pitfalls. Rewriting large codebases in safer languages is an extremely difficult task in software engineering. Even with cutting-edge intelligence, AI-generated migrations may also be unreliable, introducing many new bugs. Formal verification is not a silver bullet; its effectiveness depends on how well the specifications are written. Even systems like Lean can still have kernel-level reliability bugs that undermine mathematical guarantees. To get these right requires careful architectural design, strictly defined specifications, and extensive penetration testing of the results.
2. Security "Disappears" into Applications
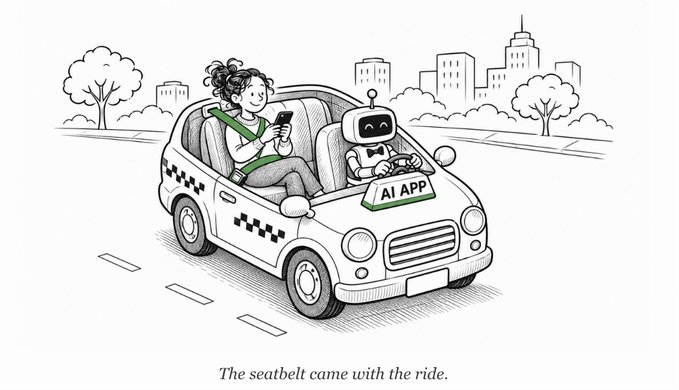
For consumer applications, privacy and security may ultimately "disappear" into those applications that initially win through convenience and developer experience, rather than as a separately paid product. Cryptographic wallets as a service are reinforcing key management in this way. Privy and Turnkey hide the cryptographic complexities behind trusted execution environments and multi-party computation, making integration easy with friendly user experiences. Agents might take the same path: more secure defaults arrive through better applications and development tools, rather than relying on separate purchases of security. Security becomes like a seatbelt in a taxi—the passenger chooses this ride for convenience, and protection is built in.
Zero-knowledge proofs and TEE may already be quietly spreading this way. World ID has already completed "human verification" for over 18 million people, allowing enterprise teams to show which participants in a Zoom call are verified humans. WhatsApp’s Incognito Chat runs Meta AI conversations within a TEE, and Meta claims even they cannot access them. In these two examples, the cryptography is hidden behind familiar apps, so users shouldn't feel like there's an extra step.
At the same time, private and local models may also be a path toward embedding privacy in products. By 2026, open-source weight models are only about four months behind proprietary cutting-edge ones. Smaller models are becoming increasingly capable, and device chips are getting stronger, meaning local inference may claim a larger share of AI tokens. Inference is moving from the cloud to the edge, and the nature of security threats will also change. Sensitive data may move less off devices, shrinking leaks of this type. However, compromised laptops or home servers could also become hosts for trusted agents, shifting the attack surface to hardware controlled by the user. This could be beneficial for local agent operating environments—models, tools, logs all on the same hardware, even potentially creating space for new hardware and software forms to run home or team agents.
3. The Dual-Lane Internet
Agents and humans browse the internet very differently. As agent traffic grows, the network is splitting into two lanes: one lane dedicated to agent-only browsing, supported by systems like Parallel, Browserbase, and Kernel; the other lane for humans, routing requests based on who is making the request and what it is. Website owners can use these identity checks to filter traffic and set transaction permissions while not completely blocking agents. Just as a restaurant can serve both takeout and dine-in customers from the same kitchen, a website can provide the same content in different formats to different requesters.
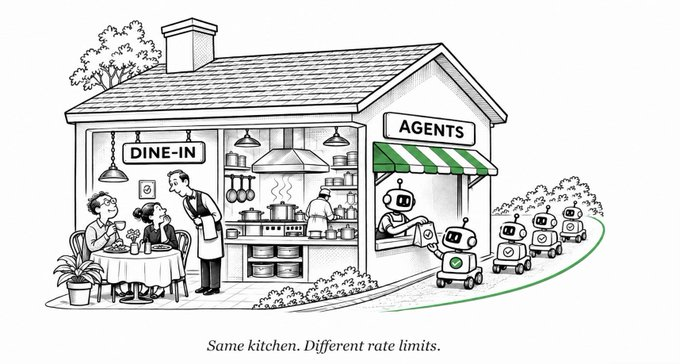
Looking further, agent lanes may increasingly consist of conversations between agents. Once both consumer agents and enterprise agents become common, my Instinct or Muse agent might seek out DoorDash's text-ordering agent to negotiate a personalized price and experience. There are already early cases of agent-to-agent relationships, such as Anthropic’s Project Swap experiment. In these scenarios, each agent knows something about its principal that others do not, so it decides what preferences and information to disclose, requiring security safeguards: what agents can promise, transaction records, and the ability for after-the-fact arbitration and auditing.
In this complex agent-to-agent negotiation, simply knowing the agent’s identity is not enough. Principals and counterparties want to know how the agent has performed previously: whether it has paid, whether it kept its promises, and whether it leaked any secrets. Portable agent reputations may be an important supplement to agent identities. But this also raises a question: who will maintain agent reputations across applications, and how can we prevent this from becoming another centralized control point?
4. Moving Toward an Anti-Fragile Internet
If this recent wave of agent-led hacking attacks has taught us one thing, it is that everything can be hacked. There will always be new bugs and new attacks, and cutting-edge agents will find many of them first. The internet is anti-fragile not because we won't face these threats, but because of how we respond, how we adjust the system. We need to design proactively to prevent, execute patches on discovered vulnerabilities, and continuously upgrade our systems and toolchains.
In practice, this may resemble a security loop. Cutting-edge models run offensive security tests around the clock, with the issues found not only flowing into better codebases but, more importantly, into improved toolchains and programming languages. All of this is connected by an agent developer stack that rapidly discovers, fixes, and migrates codebases. Ideally, formal verification could also be built at the compiler level, with its assumptions and proofs undergoing penetration testing by the same set of cutting-edge attack models. Each discovered bug can feed back into the data loop, making the entire internet more robust.
Looking at the larger picture, this permissionless, autonomous, anti-fragile internet shares similarities with many of the original visions of blockchain and cryptocurrency. USV has explored and invested in this direction for a decade. Blockchain has demonstrated how strangers can interact securely without mutual trust, starting from the most trust-dependent asset: money. But cumbersome development and infrastructure costs have limited this vision from breaking out of finance. As agents make the internet more complex and involve more parties, we might have another opportunity to embed cryptographic ideas into the applications and protocols that people are already using. For instance, DAOs vaguely show what future multi-agent clusters could look like.
Looking back, the original design of the internet was that with each additional node, the whole system became more robust. Agents pose a threat to this design but may also be the very way we restore it. At USV, we want to bet on the anti-fragile internet in three directions. First, we maintain our consistent theme of “eliminate, not automate,” supporting those methods that eliminate entire classes of bugs from the start rather than relying on after-the-fact detection and patching. Second, we extend our argument that “data is at the edge,” believing that agent security logs have real network effects: whoever captures these logs can create safer products than others. Third, we view agent security as a part of the “rebels’ alliance”—building tools, workflows, and protocols that integrate security into friendly consumer interfaces and seamless developer experiences.
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到[email protected],本平台相关工作人员将会进行核查。


