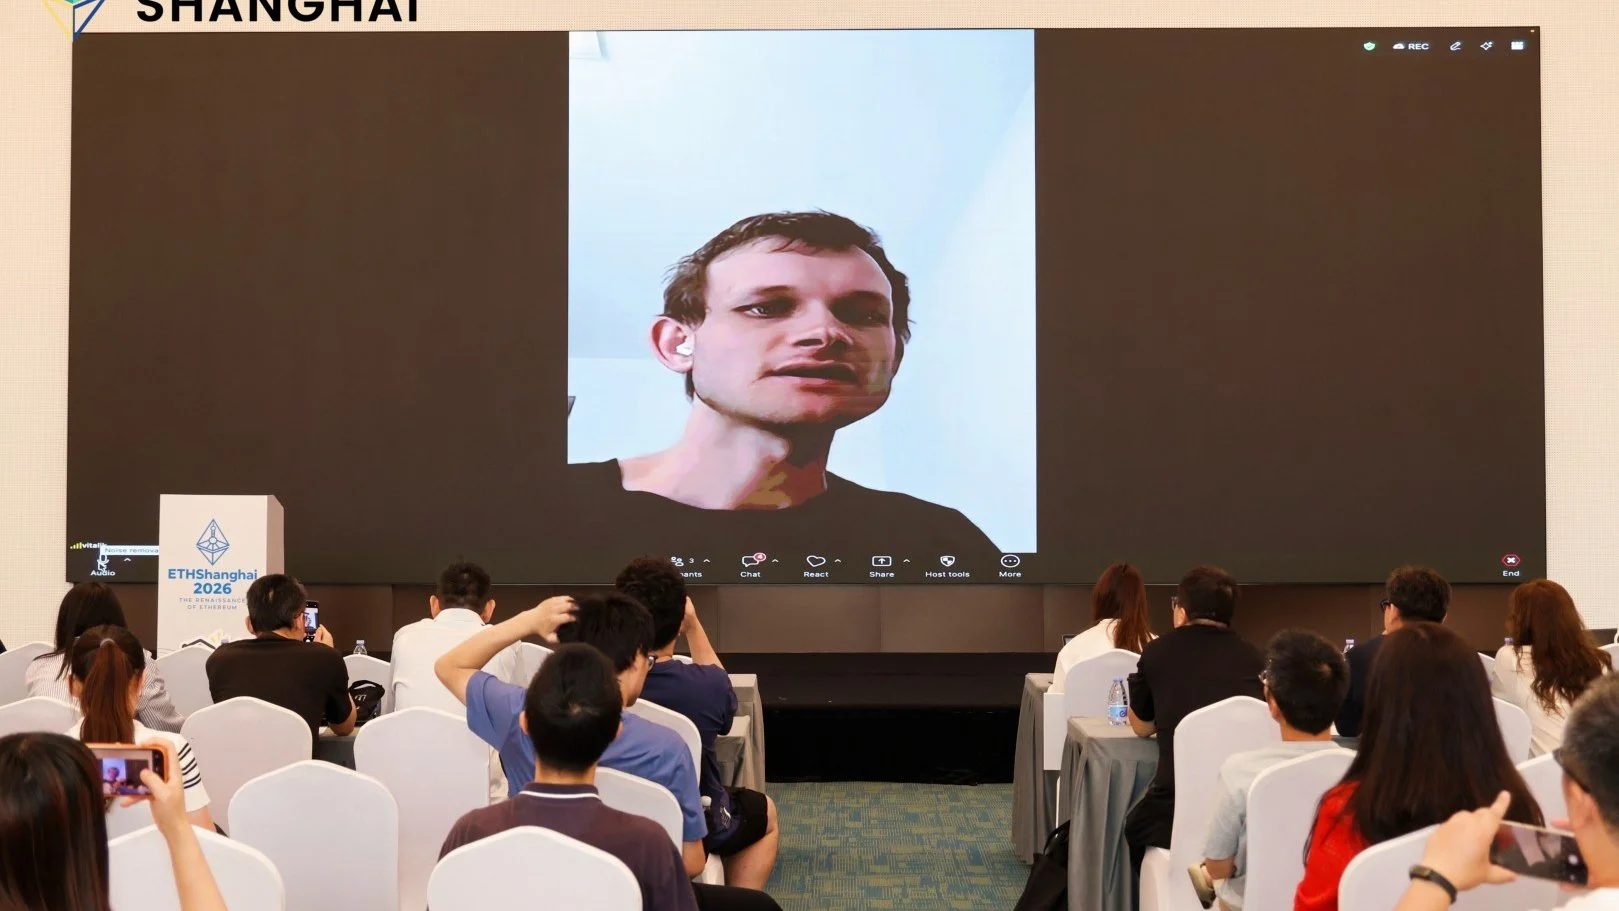
Speaker: Vitalik Buterin
Translation: Jae, PANews
Twelve years ago, when the first Blockchain Global Summit kicked off in Shanghai, Bitcoin was merely a technical experiment lurking in geek mailing lists, and the Ethereum white paper had yet to be born. The term "blockchain" was still too unfamiliar to the vast majority of people.
In the same venue, twelve years later, Ethereum founder Vitalik Buterin depicted a new form of "Blockchain + Cryptography" on the big screen. The intrusion of artificial intelligence has further accelerated this technological revolution to new heights.
Below is the edited full text of Vitalik Buterin's speech.
Change in Fifteen Years:Similar on the Surface, Different at the Core
Today, I want to discuss a macro topic. We have been discussing blockchain and cryptocurrencies for more than 15 years. Blockchain activities in Shanghai have also been ongoing for over a decade. Bitcoin was born in 2009. On the surface, the tools and technologies we are building seem to remain similar, but in reality, there are many differences that have emerged over the past 15 years. These differences are crucial.
One reason is that the types of assets you gain as a user and the types of costs you bear are vastly different. Ten to fifteen years ago, even our views on goals and the objectives we tried to achieve have significantly changed.
Fifteen years ago, blockchain was our primary tool. Bitcoin combined blockchain, signatures, and proof of work. Ethereum added smart contracts and transitioned to proof of stake in 2022. These were the tools we utilized at the time. So, what characteristics did you gain from using blockchain?
Firstly, blockchain is open, and anyone can freely participate; it is global, reliable, secure, and neutral. No centralized actors can interfere with your applications, prevent them from running, or force them to give incorrect answers.
Zooko, who created Zcash, likes to say: public blockchains are like Twitter for bank accounts. When the Bitcoin white paper was released in 2009, people believed that the basic answers to these questions were: personal names would not be directly linked to their transactions, and if there were strong privacy protections, it was somewhat acceptable. But now, we possess extremely powerful data analysis capabilities and remarkably powerful artificial intelligence, and that answer is no longer valid.
Meanwhile, people want chains to do more things. They want them to have stronger performance. People are not only interested in payment functions but also want those payment functions to have more powerful and superior characteristics. Therefore, we both want to move further. In many areas, we indeed need to move further.
Zero-Knowledge Proofs: From Roadmap to Main Battlefield
The biggest changes have occurred in the technological realm. Over the past decade, we have experienced the rise of zero-knowledge proofs, including SNARK, and then the quantum-safe version of SNARK: STARK. The role of these constructs is that they allow you to verify a computation: one person runs the computation, generates a proof, and everyone else verifies it. The computation occurs in this way, making the verification process vastly more efficient.
Moreover, it does not need to disclose all information, that is, all information used for the computation. Therefore, the core part of blockchain technology relates to this issue: the issue of verification. We want a system where everyone can participate, and everyone can be assured: what is happening follows the rules.
The initial technology required everyone to redo all operations. Thus, you sacrificed scalability and privacy. SNARK and STARK changed both of these aspects. We’ve been talking about it for ten years, but it is gradually approaching reality every year.
I believe the biggest change this year is that all plans will shift towards these technologies. They are no longer part of the future nor merely a part of the roadmap. There are now EIPs, such as EIP-8288. We hope it can integrate STARK, potentially in two years, and perhaps combined with artificial intelligence, or even sooner. They form the “strawman roadmap,” where everything within will utilize STARK after the upcoming forks occur in the next two years, becoming ubiquitous. Thus, this is a significant change.
Another significant change is that now there are more powerful technologies available. I believe these technologies are also on the verge of being realized. For example, fully homomorphic encryption, or FHE, is already in use by many. Additionally, obfuscation techniques and IO technologies, many thought to belong to a distant future, are actually becoming increasingly feasible within a shorter timeframe, faster than many imagined. So we have more powerful technologies.
These powerful technologies bring us many things. For instance, one of them is: you can parallel process the blockchain. Parallel processing starts before transactions are included in blocks.
FOCIL:16 Participants and Proof Aggregation
FOCIL is an EIP that is entering START (sound). This is the first instance of multi-party participation in block construction occurring on Ethereum. Therefore, blocks are not created by a single participant but collaboratively by 16 participants and finally completed by one ultimate builder. Its goal is to provide stronger assurances: if you send a transaction, that transaction will be included in the next slot. Thus, no single actor has the power to delay it.
In addition to fossil fuels, there are EIP-8288 and EIP-828H (sound). These indicate that you have substantial proof that these very large and costly objects are happening. We actually do not need to directly place them into the blockchain. Instead, they can be processed in large-scale parallel processing to prove all proofs, and this process happens off-chain, in the memory pool, in the gaps in between. When you send a transaction, once that transaction is on-chain, in that space, it will replace all objects, proving their existence with just one proof. Therefore, many changes have occurred in the field of cryptography technology.
But I believe the significance of these changes lies in how we have truly changed our mindset: what is the goal for such systems?
Programmable Cryptography: From“Who Can Send What”to“Who Can See What”
First, an important question is: what are we protecting?
Bitcoin signifies that we are protecting a type of data asset, namely “Bitcoin currency.” If you can issue your own digital assets, we can protect them too. Utilizing modern cryptographic assets and information, in Bitcoin and Ethereum, cryptography and code output an answer to the question: “Who can send what?” Which asset belongs to whom? Who can send which asset when?
Now, we are entering the age of programmable cryptography. Here, the code determines who can see what. So, who can see what information, not just who can send it, but also who can see it? This is becoming programmable. Where does the computation occur? Fifteen years ago, blockchain was merely blockchain.
In the next five years, I believe this will largely accelerate. We are speeding up, in this regard: not merely having a blockchain but embracing this entire channel, this vast cryptographic network. It contains the full channel: users perform a large amount of computation locally, completing most work before the data leaves the user's device; then the transactions go through a mining pool, which comes in various types with differing privacy attributes; then it gets aggregated, with several different types of participants, and block building occurs, then recorded on-chain.
Now, in this mechanism, a vast number of the same transactions are being reprocessed, handled by each node. In Ethereum, a proof was verified numerous times.
What Is Sacrificed: Latency, Scalability, and “Scalable Universality”
Finally, what do we sacrifice?
I think this is a good point. If I sacrifice scalability, I also sacrifice latency. Centralized systems can provide latency of 100 milliseconds, sometimes even reaching 300 milliseconds. Globally, the final confirmation of Bitcoin still takes ten minutes. Currently, Ethereum takes 12 seconds to generate a block, with approximately 16 minutes needed for final confirmation.
But in the future, even theoretically, according to the current roadmap, it is expected to reduce to 4 to 8 seconds per block and 8 to 32 seconds for final confirmation. And scalability is a major transformation. Specifically, blockchain architecture will no longer always require such significant sacrifices.
In terms of scalability, it will sacrifice, but not scalability itself, rather scalable universality. It will sacrifice the capability for extremely high scalability computation. If you don’t impose any limitations on this system, nor provide assurances to regulate its computational behavior; if you have computational power and can package it, split it into two parts where they can be executed separately, verified separately, and run. Before anything happens, even before entering the chain, then extremely high scalability actually becomes feasible.
Therefore, if you consider the blockchain, view it as a complete system, including L1, L2, and also the memory pool, L2, tools. All these systems transform into a highly complex intermediary layer. You or your agents can solve it. Because artificial intelligence is helping to make them more refined. But essentially, every workflow stage is being accelerated, accelerated by artificial intelligence.
So, before artificial intelligence emerged, we had zero-knowledge proofs, but they only had very simple cryptographic applications, which were viable in possible cases. One of the reasons is that if the number of code lines exceeds about 100 or 1000, then there is nearly a certainty that there will be vulnerabilities.
AI and Formal Verification: Bringing Down “100x Overhead”
We believe we can utilize it for verification. We can use different types of redundancies, tests, specifications, and analysis to create more significant and complex things. For instance, in the post-AI era, we can encode everything, everything we do, in cryptography. Also, the algorithms we use have high overhead. Now, a 100x overhead, or even lower, is often possible.
Therefore, for ZK-SNARK, we have achieved less than 10x overhead applied to AI reasoning. We’ve achieved under 10x overhead for certain types of hash operations. Then we have FHE/FLoC (shorthand), which I estimate is about 250x overhead, but in reality, this figure is rapidly decreasing.
Before verifying all these, it was manual operation. Now, formal verification is another significant operational bottleneck. This is one of the main reasons why L2 has failed to meet expectations. Thus far, it is due to a limitation: the degree to which you protect them is limited, so you need redundancy, you need multiple verification systems, you need security councils.
And the new technology is formal verification. If necessary, you can even use multiple specifications corresponding to an implementation. Therefore, you can express what is being done using different methods, different people, different agents, different teams. Then you automatically and mathematically prove that they all express the same meaning. If what they ultimately express is different, then your foundation will be much smaller. Everyone can refer back to it, better understand which party is correct.
Therefore, great progress is happening, massive advancements in the Ethereum world, including both protocol and application level. I encourage everyone to visit our website at drawmap.org to check the Ethereum protocol. If you look closely, you will find that every bit of hard work, about a year later, will be involved in this: very advanced cryptographic functions, placing everything inside STARK, everything within the virtual machine, aggregation, formally verifying everything, deploying quantum-safe signature algorithms. All these factors combined will transform theory from mere blockchain into a larger network that includes different tiers.
One of the advantages, I believe, is that artificial intelligence not only helps us build all these things faster but also helps us build them more securely.
Security, Understanding, and Contribution: The Frontier Becoming Approachable
Of course, security is what we genuinely choose to focus on, and this is indeed a concern in Ethereum. But artificial intelligence, I believe, also makes it easier for everyone here to understand all these things.
So I want to say, if anyone here is a developer or a researcher, I would genuinely encourage people to attempt to understand the different pieces being constructed, thus understanding the different components, and figuring out what properties those various components possess, and try to determine if there's any specific part that you want to or can contribute to.
I believe a nation can contribute to this frontier area, including technology and ecosystem, which is rapidly becoming more feasible and more accessible to anyone. Or rather, for those willing to learn, willing to think, and willing to invest energy in helping, assisting in research, and helping construct. There are even open competitions ongoing aimed at improving and formally verifying improvements to many algorithms.
Moreover, this is also a good time to truly rethink applications, that is, the applications we have long been doing, and to build new applications. These are all applications that are built on Ethereum. Five years ago, ten years ago, fifteen years ago, many of them were not constructed with the mindset that these new technologies are feasible, that privacy can be programmed, and that even complex code security can be guaranteed. Now all these have become possible.
So I encourage people to immerse themselves in development, to develop applications, combine them, namely Ethereum and other decentralized networks, and other things in the real world, just as you wish, to influence, to improve.
Thank you!
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到support@aicoin.com,本平台相关工作人员将会进行核查。


