Author: Lithos.eth
Translated by: Deep Tide TechFlow
Deep Tide Guide: The public ledger of Bitcoin not only breaks the monopoly of traditional financial intermediaries but also exposes all transaction inputs, outputs, and amounts without reservation under the spotlight. Satoshi Nakamoto pointed out this architectural flaw clearly in Section 10 of the white paper, suggesting the use of anonymous public keys as a defense, but this is merely a pseudonym, not true confidential transactions.
From early blind signatures and zero-knowledge proofs to on-chain confidential transfers of Monero and Zcash, and then to Aztec and Oasis Sapphire's programmable privacy in smart contracts, as well as Ethereum's Kohaku for solving wallet inquiry leaks, the crypto world is moving out of the single mixing coin trap. Privacy is by no means about covering everything, but rather about empowering individuals with the selective power to showcase their data to the world.
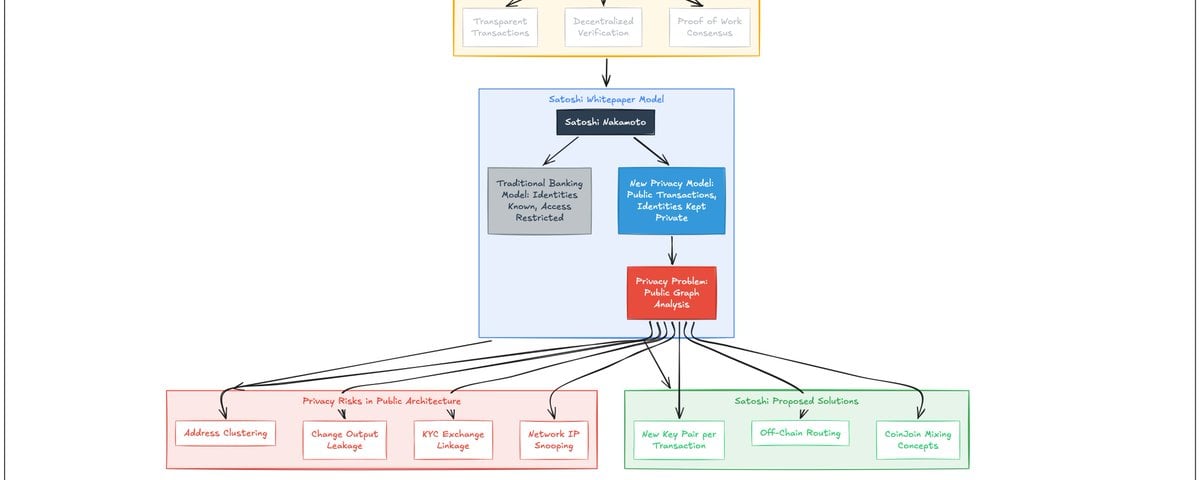
Bitcoin allows anyone to independently verify the complete transaction history without seeking permission from a bank.
However, such a publicly visible record may leak personal privacy far beyond user expectations. Satoshi Nakamoto had already explored this tricky issue in Section 10 of the original Bitcoin white paper.
Since then, researchers and developers in cryptography have continuously explored technical paths that can protect information secrecy while maintaining transaction verifiability. After years of evolution, how far have we come today?
When you pay someone with Bitcoin, the moment the payment is confirmed, that transaction becomes an indelible part of the global public ledger.
Anyone in the world can access it at any time.
They can see the input source of every expenditure, the output address receiving the funds, the specific amounts distributed to these outputs, and the block height and timestamp of when the transaction was packed and confirmed.
Analysts may not initially know your real name, but as long as one of your addresses is linked to an identity in the real world, all your past and future on-chain activities become incredibly easy to track.
Your salary income, savings scale, business payment exchanges, and daily consumption habits may leave traces on the same public ledger.
For a system originally intended to enable individuals to freely transfer funds outside the banking system, this is undoubtedly a thought-provoking compromise and trade-off.
Moreover, Satoshi Nakamoto did not overlook this. In the initial Bitcoin white paper, the title of Section 10 is precisely "Privacy."
To understand the future direction of blockchain privacy, we need to revisit Satoshi Nakamoto's original discourse, review the explorations of cryptographic pioneers before the emergence of Bitcoin, and objectively evaluate the advantages and limitations of various current privacy solutions.
Before Bitcoin's Birth, Pioneers Were Exploring Solutions
The discussion of privacy in digital currencies did not begin with Bitcoin.
As early as 1982, David Chaum published the classic paper "Blind Signatures for Untraceable Payments."
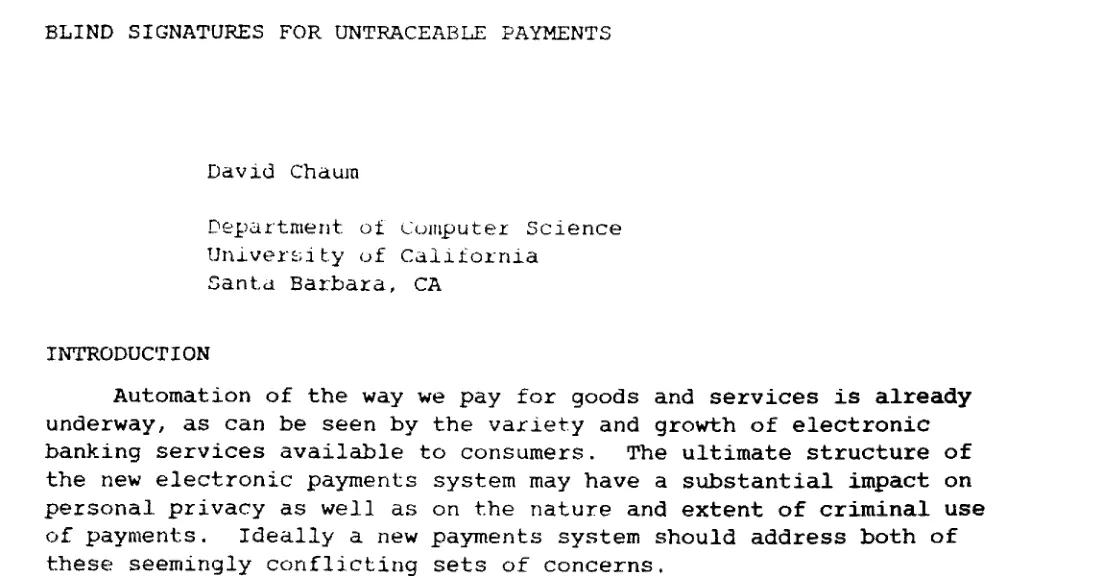
Figure: The blind signatures paper by David Chaum published in 1982, "Blind Signatures for Untraceable Payments."
In the paper, Chaum explored how users can obtain digitally signed payment proofs without allowing the card issuer to associate the payment receipt with the final transaction.
This concept is crucial because the information revealed by a single payment extends far beyond just the transfer of funds. It also exposes who is trading with whom, when transactions occur, and the frequency of those transactions.
Chaum's research established important signposts for electronic cash, but his model still relied on centralized issuing entities. Protecting payment information and eliminating trust in centralized institutions are two entirely different challenges.
Other researchers and programmers continued to delve deeper in this direction, and the cypherpunk community was determined to make a bigger leap.
In September 1992, a group of cryptographers, programmers, and privacy advocates organized around a mailing list hosted by John Gilmore, and Jude Milhon is said to have coined the term "cypherpunk" for this group.
Their interest extended beyond digital currencies, passionately discussing strong encryption algorithms, anonymous communication protocols, digital identities, information freedom, and individuals' ability to self-protect using open-source software.
Timothy C. May wrote "The Crypto Anarchist Manifesto" in 1988 and distributed it online during early meetings of the movement in 1992.
Then, on March 9, 1993, Eric Hughes officially published the historically significant "A Cypherpunk's Manifesto."
One of the declarations still resonates profoundly today: in the electronic age, privacy is an indispensable cornerstone for an open society.
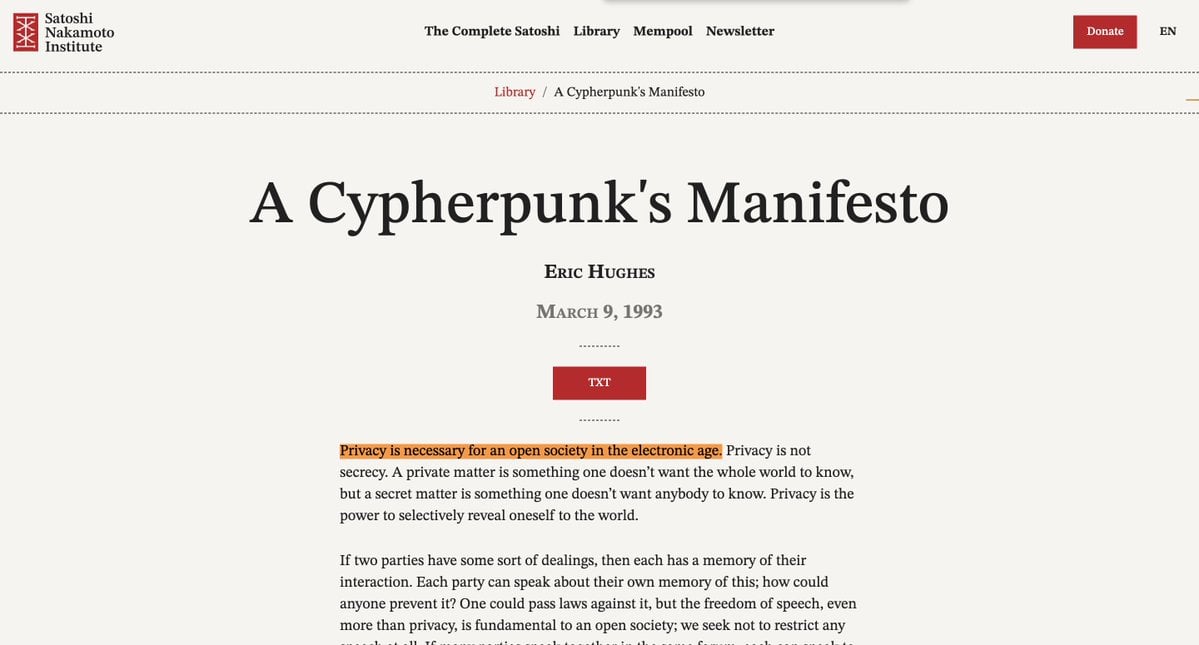
Figure: "A Cypherpunk's Manifesto" by Eric Hughes published in 1993.
But Hughes also made a more profound point relating to the examination of blockchain privacy: privacy is the power to selectively reveal oneself to the world.
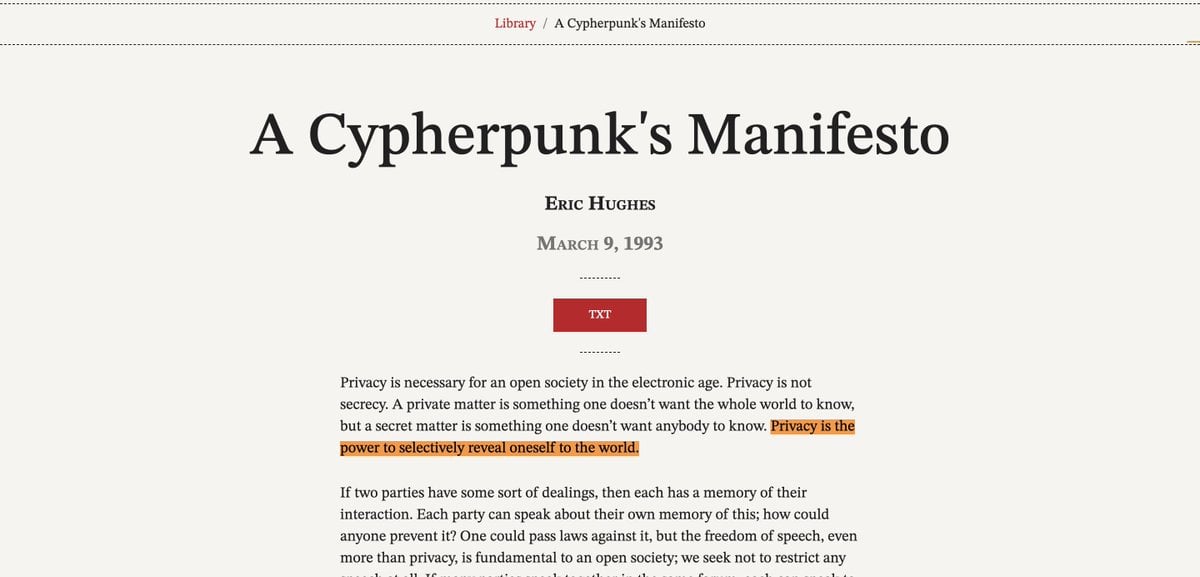
Figure: Eric Hughes stated "Privacy is the power to selectively reveal oneself to the world" in the manifesto.
He did not advocate for keeping everything hidden but emphasized that individuals must have absolute discretion over what they present to the outside world.
A merchant selling you a product does not need to examine your entire financial history; a receiver of a transfer does not need to peek into every other transaction happening in your wallet.
Hughes expressed it very clearly: both parties in a transaction should only be aware of the necessary information to complete that transaction, with no excess details involved. This concept remains central to privacy discussions today.
The cypherpunks never believed that privacy would be granted by others; they firmly believed it must be built by code. Their most well-known motto is: cypherpunks write code.
The Foundational Thought Leading to Bitcoin
The emergence of Bitcoin was certainly not a spontaneous occurrence; several pioneers had already spent years working on different technical components of digital currency.
Hashcash (Adam Back, 1997): A proof-of-work mechanism designed to significantly increase the marginal costs of spam and certain resource abuse.
b-money (Wei Dai, 1998): A design proposal for an anonymous, distributed electronic cash system.
bit gold (Nick Szabo): A proposal built around computational work to create digital scarcity, which Szabo later detailed in 2005.
Reusable Proof of Work (RPOW, Hal Finney, 2004): Attempts to make the results of proof-of-work computations transferable as digital tokens.
These explorations, while different, did not directly evolve into Bitcoin, and each solved different problems, but they outlined the profound academic and ideological foundation in which Satoshi Nakamoto was situated.
At that time, the industry had already shaken off a serious technological wave, trying to construct an independent digital currency that does not rely on commercial banks, government bodies, or centralized clearing institutions.
Satoshi Nakamoto's Bitcoin white paper explicitly cited Hashcash and b-money in its references.
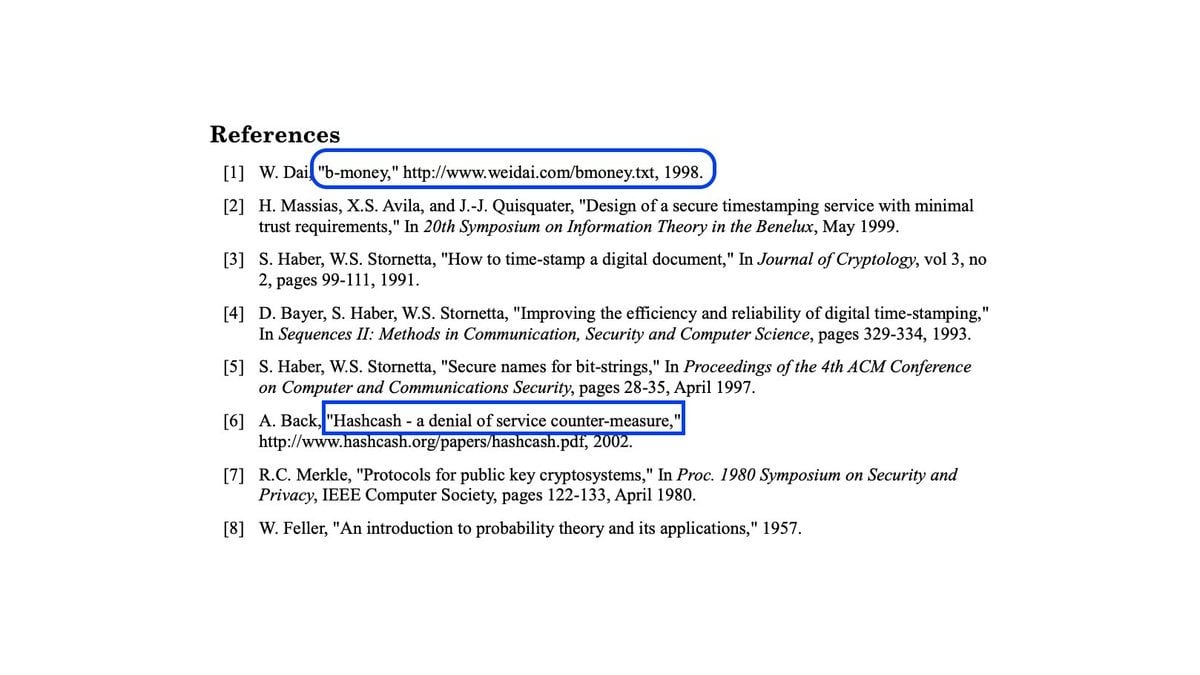
Figure: Citation of Hashcash and b-money in the references of the Bitcoin white paper.
Bitcoin embodies the wisdom of early research and tackles an extremely difficult core question: how to achieve consensus on a shared ledger without a centralized arbitration body preventing double spending?
This represents a milestone breakthrough in the history of cryptocurrency development, but the price is also evident: all transaction data must be publicly available to the entire network.
Satoshi Nakamoto's True Discourse on Privacy
On October 31, 2008, Satoshi Nakamoto released a white paper titled "Bitcoin: A Peer-to-Peer Electronic Cash System," in which Section 10 specifically discusses privacy.
This chapter begins by comparing Bitcoin's public transaction mechanism with the privacy model that people are accustomed to in traditional banking business.
In the traditional banking model, transactions are completely transparent to the bank, but the general public cannot see others' account balances and transaction histories.
The logic of Bitcoin operation is entirely the opposite: transactions themselves must be broadcast publicly to the entire network, while users' true identities are hidden behind anonymous public keys.
Satoshi Nakamoto wrote: "The requirement to publicly announce all transactions rules out traditional methods, but privacy can still be maintained by severing the information flow at another point: keeping the public key anonymous."
His specific strategy includes generating an entirely new key pair for each transaction, thereby increasing the difficulty of tracking multiple related payments back to the same individual.
However, Satoshi Nakamoto also candidly pointed out the inherent weakness of this model: when a transaction merges multiple inputs, these inputs mathematically must prove to belong to the same owner.
As long as one address is linked to a real identity in the real world, the other on-chain activities associated with that address will be traced one by one.
This is a critical conceptual distinction: Bitcoin's native design offers pseudonymity, not true confidentiality. Your real name is not directly recorded in the ledger, but the details of every transaction on-chain are exposed, and auxiliary data from off-chain is sufficient to match on-chain addresses with real individuals.
Satoshi Nakamoto never claimed this is perfect privacy; he merely proposed a pragmatic compromise to minimize the association between transactions and real identities in a distributed system that relies heavily on public verification.
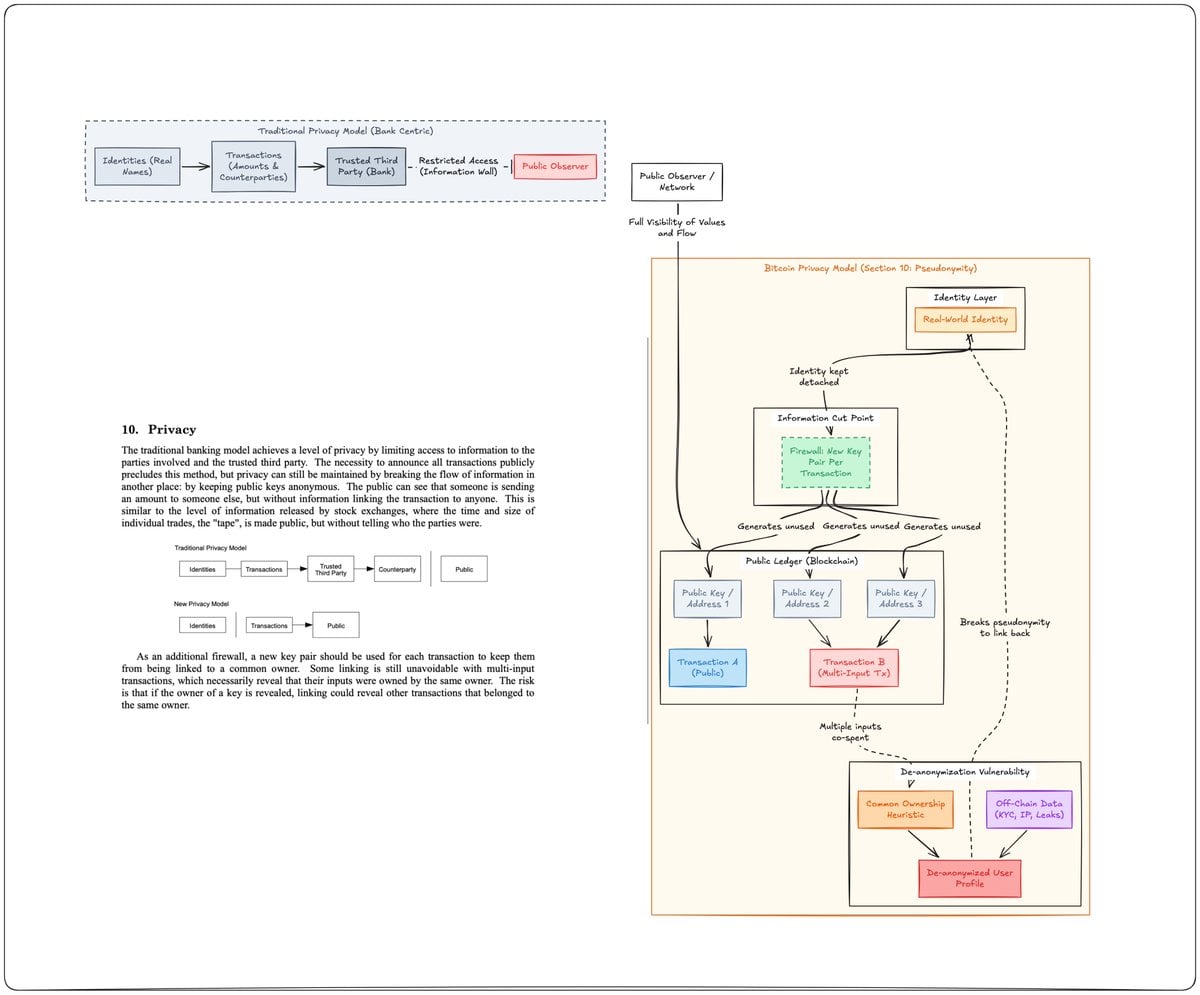
Figure: Comparison of the traditional privacy model and Bitcoin's new privacy model drawn by Satoshi Nakamoto in Section 10 of the white paper.
What Can Others See from a Bitcoin Transaction?
Let's look at a specific everyday payment scenario.
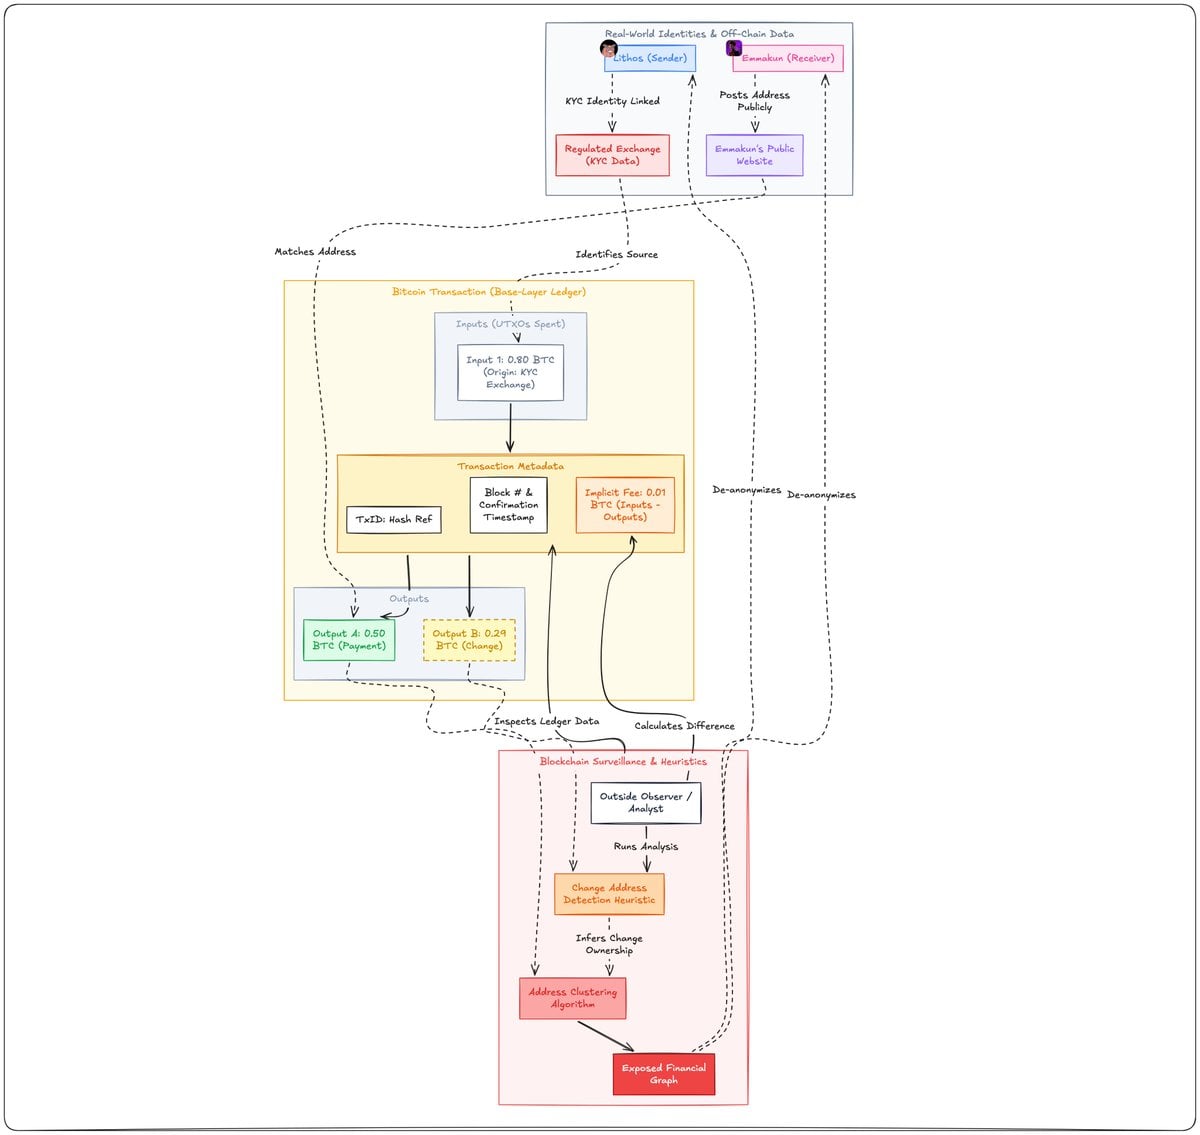
Lithos intends to pay Emma 0.5 BTC, and he constructs a payment transaction using the unspent transaction outputs (UTXOs) he already has.
This transaction is broadcasted to the entire network, packed into a block, and permanently recorded on the blockchain ledger.
At this point, any external observer can clearly verify the following elements:
· The specific input UTXOs spent in this transaction;
· The target output address receiving the funds;
· The exact Bitcoin amounts allocated to each output;
· The transaction fee (accurately calculated from the difference between total input and output amounts);
· The specific block height and timestamp when the transaction was confirmed in the block.
Observers may initially not know the real identities of Lithos or Emma.
But suppose Lithos’ funds come from a compliant exchange that strictly implements real-name identification, or Emma has publicly disclosed her donation address on her personal webpage.
Then on-chain analysts can easily lock in these addresses to real identities and trace their entire historical transaction trajectory.
In reality, there are also complexities from change outputs: when a transaction produces change, funds typically return to the sender rather than being paid to the receiver.
On-chain analysis firms often rely on specific algorithmic assumptions to guess which output is change; although these heuristic rules are not always accurate, they are enough to outline a valuable flow diagram of funds.
The key conclusion is this: even if Bitcoin never directly records names, its fully transparent transaction history can still expose a large amount of sensitive personal information.
This is exactly why we must never confuse "anonymity" with "privacy" when discussing Bitcoin. Its addresses are pseudonymous, while its underlying transaction history is entirely public.
Satoshi Nakamoto Was Still Contemplating Privacy Issues in 2010
There is a particularly enlightening episode in the history of Bitcoin development.
On August 11, 2010, Satoshi Nakamoto participated in an in-depth technical discussion titled "Not a suggestion" on the BitcoinTalk forum.
The core topic at the time was: can Bitcoin avoid storing all transaction history data completely as it initially did?
The bottleneck of this consideration lies in preventing double spending: if a network node does not possess enough information to trace the entire transaction history, how can it confirm that a particular coin has not been spent before?
Satoshi Nakamoto explained that the validation of the nonexistence of double spending logically requires nodes to have global awareness of all relevant transactions across the entire network.
He then wrote a profoundly significant statement: "In this situation, it's hard to think of how to apply zero-knowledge proofs."
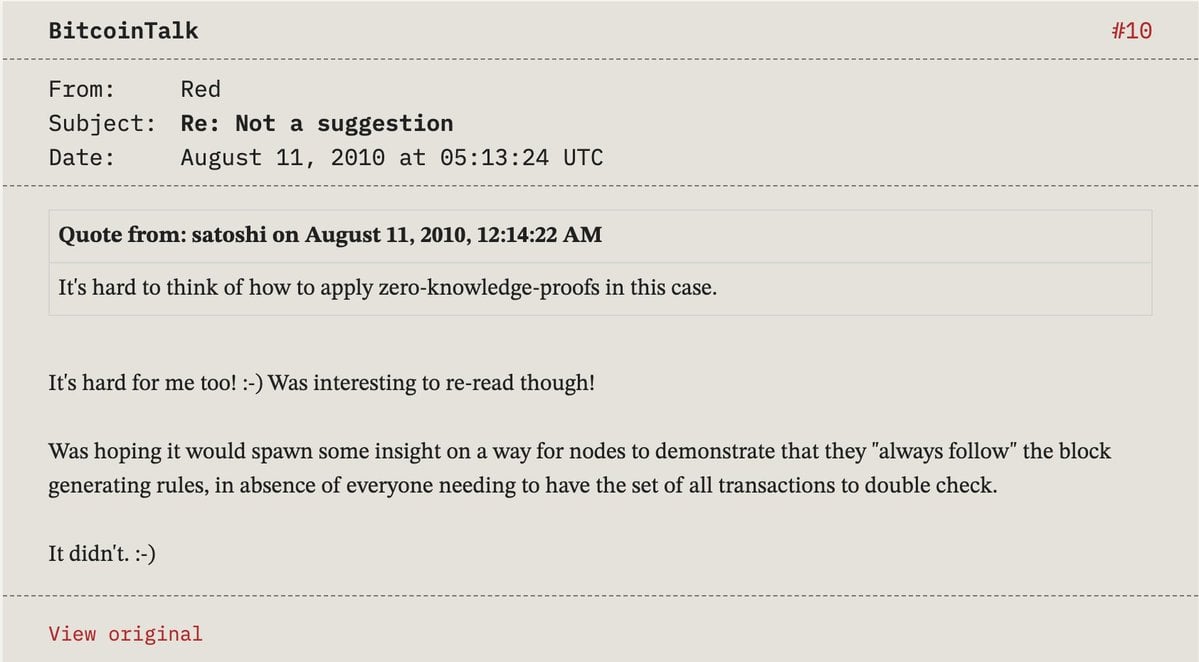
Figure: Satoshi Nakamoto's discussion on zero-knowledge proofs and double spending verification on BitcoinTalk in 2010.
The context of this statement is critically important: Satoshi Nakamoto did not believe that zero-knowledge proofs were useless; he was exploring a specific technical dilemma: how can nodes prove that an asset has never been double-spent without having complete transaction history?
In other words, how can the network verify some "nonexistence"? This is a completely different technical dimension from "can the proof hide the detailed parameters of a payment."
Clarifying this historical detail is crucial because many contemporary discussions on privacy often mistakenly assume that Satoshi Nakamoto completely ignored zero-knowledge cryptography back then.
The historical facts are far more nuanced than rumors: Satoshi Nakamoto not only understood the concept of zero-knowledge proofs well but also deeply contemplated the massive engineering challenges of applying it to Bitcoin's double spending verification.
The following explorations in cryptography rooted themselves in this soil: researchers established a new paradigm of utilizing zero-knowledge proofs to conceal transaction details while still allowing all network nodes to verify the legality of transactions.
From Concealing Identity to Concealing Payment Details
The progress in cryptography research did not cease with the maturity of Bitcoin.
In 2013, the academic community published the groundbreaking paper "Zerocoin: Anonymous Distributed E-Cash from Bitcoin."
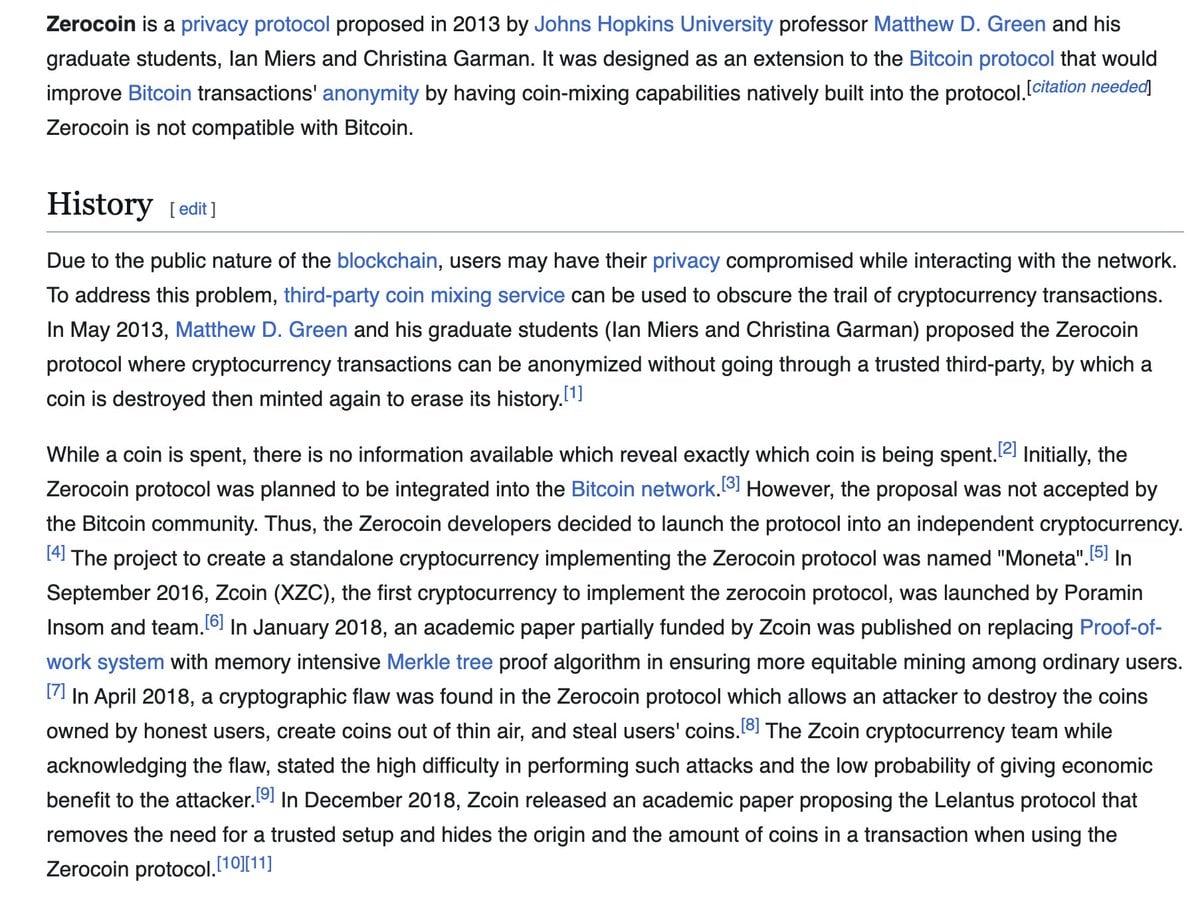
Figure: The 2013 paper "Zerocoin: Anonymous Distributed E-Cash from Bitcoin."
The paper accurately pointed out Bitcoin's critical flaw: the fully public ledger structure means its privacy protection is entirely built upon fragile pseudonymity.
Zerocoin explored how to use cryptography to break the association between transactions and their origins, but it would still expose the destination of payments and the amounts transacted, thus having obvious limitations in payment flexibility.
By 2014, the research team advanced further, launching "Zerocash: Decentralized Anonymous Payments from Bitcoin." Zerocash introduced non-interactive zero-knowledge proof technology zk-SNARKs, successfully creating a comprehensive protocol that could conceal the sender, receiver, and transaction amounts while allowing network nodes to verify the validity of transfers tightly.
This represented a profound enhancement to Satoshi Nakamoto's original privacy model.
While Bitcoin tried to decouple public addresses from real identities, Zerocash sought to completely hide transaction data from public view.
This was a milestone shift: decentralized networks do not need to know every plaintext detail of a payment to confirm whether it adheres to monetary rules.
With concise zero-knowledge proofs, the system can mathematically prove the legality of a transaction to the entire network without disclosing the construction parameters of the transaction.
This is also the core reason why zero-knowledge cryptography has become the crown jewel of blockchain privacy research.
What Do Contemporary Mainstream Privacy Systems Actually Protect?
In everyday discussions of blockchain privacy, people often confuse all projects as one.
But hiding the recipient does not equate to hiding the amount; hiding the amount does not equate to hiding the on-chain transaction topology; and hiding on-chain data does not automatically eliminate the risk of data leaks from network communications before transactions take place.
We need to clearly separate and analyze these technical factions.
Some systems can hide the receiver while keeping the amount public; some systems conceal the transaction amount while exposing traces of inquiries at the wallet or network RPC nodes; while others allow users to prove compliance without disclosing their entire identities.
These belong to completely different dimensions of security, and we can look at a few representative technological implementations.
Bitcoin and Payjoin
While Bitcoin maintains transparency at the foundational ledger level, this does not mean developers are doing nothing regarding privacy improvements.
Community developers have designed a mechanism that significantly reduces the reliability of traditional on-chain graph analysis, among which BIP 78, defined Payjoin, is particularly representative.
Payjoin allows the payer and the payee to collaboratively build a payment transaction, with the payee also actively contributing an input UTXO to this transaction.
Why is this crucial?
Traditional on-chain tracking analysis usually relies on a core assumption: all input addresses in a transaction belong to the same person. However, if the payee also injects an input in a Payjoin transaction, this general assumption becomes completely invalid.
Payjoin does not hide the transaction amount, nor does it transform Bitcoin into a confidential payment system; it simply greatly increases the difficulty and uncertainty for external parties to perform on-chain fund aggregation analysis.
This improvement is very practical but should not be confused with end-to-end completely confidential transactions.
Monero
Monero has taken a different approach, embedding strong privacy protections directly into its underlying transaction mechanism by default.
It operates through several core cryptographic components that comprehensively conceal every dimension of a single payment:
· Ring Signatures: Obscuring the real sender, making it impossible for external observers to discern which output was actually spent from the obscured ring;
· Stealth Addresses: Generating one-time target addresses for each payment, severing the connection between the transfer and the recipient's public address;
· RingCT: Encrypting and hiding the specific amount of the transaction while still allowing the network to validate the currency issuance and conservation laws.
However, this system also has boundaries: the sender's privacy possesses probabilistic attributes, depending on the settings of the transaction ring and the auxiliary data that external observers can access.
Monero also introduced the Dandelion++ protocol to reduce the traceability of transactions when broadcasting in a P2P network, but its official documentation clearly warns: this still cannot resist all network-level listening.
Users' broadband service providers, VPN service providers, or malicious remote nodes may still collect network-layer interaction signals.
Zcash
Zcash has transformed the academic research achievements of Zerocash into a mature encryption asset system.
Its core weapon is shielded transactions, relying on zero-knowledge proofs to conceal core transaction information.
In transfers between shielded addresses, the public ledger does not expose the sender, receiver, transfer amounts, or remarks content; the network nodes merely need to verify the zero-knowledge proof to ensure asset legality.
This provides stronger on-chain confidentiality protection compared to Bitcoin's original pseudonymous model.
However, Zcash also retains transparent addresses, and interactions involving these addresses remain completely visible to the outside world.
The usage rate of shielded transactions, the path of funds flowing between transparent pools and shielded pools, different wallet support situations, and the overall size of the anonymity set directly determine the level of privacy protection users actually obtain.
Additionally, Zcash also introduced an observation key mechanism that allows users to disclose transaction details to specific auditors without giving up the power of asset spending, showcasing the design philosophy that "privacy and disclosure are not a zero-sum game."
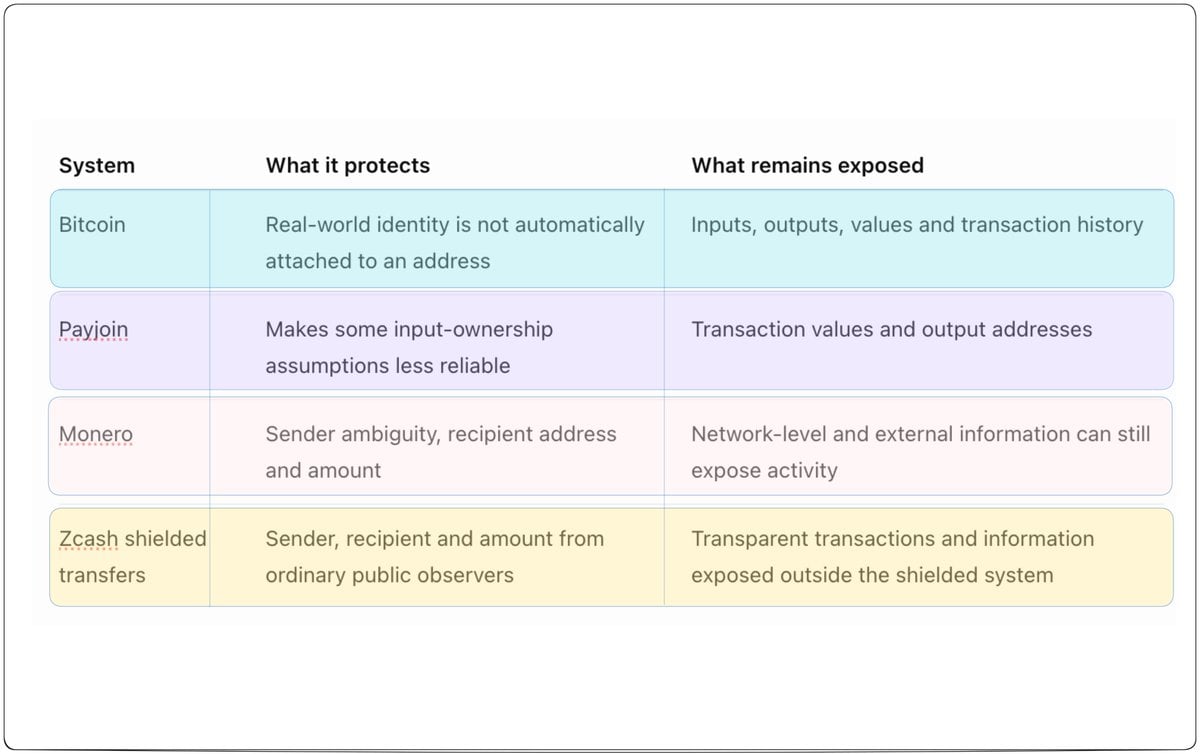
Figure: Comparison of on-chain privacy features of Bitcoin, Payjoin, Monero, and Zcash.
It is important to emphasize that the above comparison only describes the on-chain information that external observers can obtain from the blockchain ledger and does not cover risks from off-chain dimensions such as IP address leaks, device hacking, or real-name aggregation by exchanges.
Privacy is by no means a single static function, but rather a set of collaborative, multi-layered defenses.
New Privacy Challenges of Application Layer Smart Contracts
Since the birth of Bitcoin, the industry's biggest evolution has not only been the development of tokens that conceal transaction details but also the integration of privacy concepts into the design genes of smart contracts and decentralized applications.
Today, people’s on-chain behaviors go beyond simple transfers: lending and staking, decentralized trading, DAO governance voting, asset allocation management, and qualification proving.
These interactions release sensitive commercial and personal data: traders do not want their hidden positions to be followed in real-time by the entire network, companies do not want their treasury fund flows to be transparently visible to competitors, and ordinary users need to prove eligibility without revealing their entire real identities.
Programmable confidential smart contracts were created to resolve this contradiction, with the core goal of enabling decentralized applications to efficiently execute complex operations without having to make every piece of data involved in the process publicly available.
The industry is currently breaking through in different architectural dimensions:
Aztec: Layer 2 Balancing Privacy and Public Functions
Aztec is committed to building a privacy-focused Layer 2 on Ethereum, allowing developers to flexibly mix declaring private functions and public functions at the code level.
The core dividing line lies in where the code runs:
Private functions are executed in a privacy execution environment (PXE) on the user's local device, completing confidential computations locally and generating corresponding zero-knowledge proofs, then only submitting the proof to the network;
Public functions, on the other hand, are executed in a globally readable state across public sorters and nodes. A single on-chain interaction can smoothly connect the two.
For decentralized anonymous voting, for instance, voters complete the voting signing in a local private environment without having to publicly disclose their specific choices, while public functions unify the counting updates on-chain. The entire network can verify the final tally result's accuracy yet cannot infer each individual’s independent ballots.
However, this is not without limitations: when the local client queries network status from remote nodes, those remote nodes can still realize which data the user is interested in; hence a full node is needed to further mitigate such information leaks.
Oasis Sapphire: Confidential Contracts Based on Hardware Trusted Execution Environment (TEE)
In contrast to Aztec's client-proof-focused technical route, Oasis Sapphire employs a wholly different technical paradigm: running confidential smart contracts within a protected execution environment using hardware isolation.
The trusted execution environment relies on physical hardware isolation to protect the code and confidential data being executed. Sapphire supports fully encrypted transaction inputs and confidential internal states of smart contracts, allowing contracts to handle sensitive parameters securely.
Client-side zero-knowledge proofs and hardware TEE each have their trade-offs: TEE introduces a trust prerequisite on the hardware manufacturer’s security and microcode implementation, while zero-knowledge systems depend on complete and accurate arithmetic circuit design and mathematical proof systems.
Umbra: Focusing on Internal Transfers of Shielded Pools
In the Solana ecosystem, Umbra has demonstrated architectural innovation moving from V1 to V2.
Version 1 used encrypted token accounts to serve as intermediaries for entering shielded pools, while Version 2 has been completely reshaped into a fund circulation system centered around shielded pools, allowing users to conduct direct confidential transfers within the pools.
However, it is essential to recognize that the actions of depositing and withdrawing to and from shielded pools still leave traces on-chain; the specific amounts and timeframes of entering or exiting pools can still provide clues for on-chain analysis, with the core privacy protection focusing on the internal transfer phase.
Privacy Pools: Realizing Selective Compliance Disclosure
Developed by the 0xbow team, Privacy Pools is a compliance privacy protocol on Ethereum's multiple chains, inspired by an academic paper co-authored by Vitalik Buterin and others in 2023.
Users deposit assets from normal wallets into a shielded pool, and associated asset providers (ASPs) screen the incoming funds to exclude illicit funds, while the entire system does not implement centralized KYC or a global backdoor to view keys.
When withdrawing, users utilize zero-knowledge proofs to show that their funds belong to a screened compliant set without revealing which specific deposit entered the pool, severing the possible pollution of compliant pools by illicit funds while protecting legitimate individuals' financial privacy.
This is an excellent embodiment of Eric Hughes’ idea of selective disclosure in the modern DeFi realm: compliance and privacy are no longer mutually exclusive.
Kohaku Questions the Core Pain Point: What Do Wallets Expose Before Transactions?
In the realm of blockchain privacy, there is a crucial and long-ignored hidden danger.
A user, even if using the most advanced confidential transaction protocol, may still leak everything before a transaction is initiated due to standard network requests from the wallet itself.
When the wallet opens to refresh the account balance, it typically sends a data query to a remote RPC node, directly informing the service provider which address the user is closely monitoring.
Similar leaks frequently occur during routine operations such as querying historical transaction trails, pre-executing contract transaction simulations, or obtaining token metadata. The transaction itself may be confidential, but the network requests sent before the transaction are riddled with vulnerabilities.
This is precisely the area that Kohaku, a cutting-edge privacy project in the Ethereum ecosystem, is focusing on. As an open-source privacy-preserving wallet and SDK specification, Kohaku aims to rebuild defenses from the foundational layer of wallet infrastructure.
Kohaku introduces Private Information Retrieval (PIR) technology: in traditional balance queries, the server receives a plaintext address and returns data; within the PIR framework, the wallet constructs special encrypted queries that allow the server to return the target results without disclosing which specific account the user has queried.
The wallet is the first portal for users to manage private keys, accounts, signing permissions, and application interactions. If this entrance continuously leaks metadata, relying solely on underlying confidential transactions will never form a secure closed-loop.
Have We Surpassed Satoshi Nakamoto's Privacy Model?
From the perspective of specific technical indicators, the answer is undoubtedly affirmative.
Satoshi Nakamoto's initial design was based on pseudonymous public keys and a completely transparent transaction history. Today in the crypto world:
In terms of transaction confidentiality, Monero and Zcash's shielded transactions have achieved comprehensive on-chain concealment of inputs, outputs, and amounts that Nakamoto did not accomplish back then;
In terms of verifiable computation, modern zero-knowledge proof systems can mathematically prove compliance with complex logic to the entire network without revealing plaintext inputs;
In terms of application expansion, Aztec has brought programmable privacy contracts, Oasis Sapphire has realized hardware confidential computing, Privacy Pools has opened up compliant selective disclosure, and Kohaku is dedicated to solving wallet client inquiry leaks.
However, if asked whether the privacy issue has been entirely resolved, the answer remains negative.
A confidential transaction cannot hide physical IP leakage when broadcasting; a privacy contract cannot erase the time patterns of public function interactions; a shielded pool cannot negate the association of funds entering and exiting the pool; a TEE hardware setup cannot escape the security assumptions regarding chip manufacturers; and a sophisticated mathematical proof cannot protect a local device that has already been compromised by malicious software.
Real privacy security must cover the entire process chain: from terminal wallets, physical hardware, application interfaces, network transmission, smart contracts, to the final on-chain data.
What Should Be Public, and What Should Remain Private?
For many years, the blockchain industry has always been built on the cornerstone of global public state.
Complete transparency brings the ability for independent verification without permission, yet it also exposes the life and financial threads of ordinary individuals and business entities.
We do not advocate locking all information on the blockchain in a black box; this is precisely the core logic of "selective disclosure":
Public governance institutions and public financial expenditures must remain transparent and subject to strict scrutiny from society as a whole, and the fulfillment of network rules must allow for individual verification;
However, the private savings, salary income, everyday small payments, investment positions, and commercial contracts of ordinary citizens should never be forced to be disclosed to the entire world just because blockchain technology is used.
These two can completely coexist without contradiction: individuals can prove their eligibility to service providers without providing their entire household register; companies can smoothly settle accounts without exposing the hidden bottom line of funds to competitors; voters can cast their sacred votes while the voting results are fully subject to public audits; wallets can query assets without disclosing any specific accounts to service providers.
This is not about pursuing absolute concealment but defending the right to control one’s own data.
As Eric Hughes famously wrote over thirty years ago: privacy is the power to selectively reveal oneself to the world.
Bitcoin Unveils the Prologue, But the Journey is Far from Over
Whenever we revisit the words Satoshi Nakamoto penned in Section 10 of the white paper, the most awe-inspiring aspect is not that Bitcoin has solved all privacy issues once and for all, but that Satoshi Nakamoto from day one clearly sensed the deep tension between public ledgers and personal privacy and provided a pragmatic engineering balance under specific historical conditions.
The persistent question cypherpunks have pursued for decades remains unchanged: how can people enjoy convenience in the digital age without being forced to relinquish personal data that ought not to be exposed?
Bitcoin took the most crucial first step for this era, and subsequent researchers and engineers are continuously pioneering along this path.
When evaluating various current privacy projects, we cannot merely rely on the marketing slogans from projects, trendy cryptographic terminology, or simple "support for confidentiality" labels.
We need to calmly examine: what exactly does this system hide? What information still remains exposed to the daylight? On whose credibility are its security assumptions based? What will happen when it operates in the real commercial world?
The question initially raised by cypherpunks remains worthy of deep reflection for every practitioner: what justification does a technical system have for needing to know additional information beyond what is necessary to fulfill its essential functions?
Bitcoin allowed us to achieve the verifiability of currency without banks; and the current privacy systems work to fill the puzzle of safeguarding this verifiability while fully handing back the dignity and power of choice in how to present oneself to each independent individual.
References and Further Reading
Early Digital Cash and Cypherpunks
· David Chaum, Blind Signatures for Untraceable Payments (1982)
· Timothy C. May, The Crypto Anarchist Manifesto (1988)
· Eric Hughes, A Cypherpunk's Manifesto (1993)
· Wei Dai, b-money (1998)
· Adam Back, Hashcash (1997)
Bitcoin and Its Privacy Model
· Satoshi Nakamoto, Bitcoin: A Peer-to-Peer Electronic Cash System (2008), Section 10
· Satoshi Nakamoto, BitcoinTalk discussion: Not a suggestion (2010)
· BIP 78: A Simple Payjoin Proposal
Privacy Academic Research and Cutting-edge Protocols
· Miers et al., Zerocoin (IEEE S&P, 2013)
· Ben-Sasson et al., Zerocash (IEEE S&P, 2014)
· Monero Technical Specifications & Dandelion++
· Zcash Documentation: Addresses and Value Pools
· Aztec Network: Private Execution Environment (PXE)
· Oasis Sapphire Confidential EVM Documentation
· Umbra V2 Shielded Pool Documentation
· Privacy Pools (0xbow) Research Paper & Documentation
· Kohaku: Ethereum Privacy Preserving Wallet & SDK
· Ethereum Foundation Reads: PIR for Wallets
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到[email protected],本平台相关工作人员将会进行核查。


