Key Takeaways
- Keplr suspended Google and Apple logins on Nov. 7 following a security incident involving third-party authentication provider Web3Auth.
- Bitquery identified approximately $6.01 million in wallet transfers across multiple Cosmos networks, but some transactions involved protective recovery efforts.
- Recovery-phrase and hardware-wallet accounts remain unaffected, while Web3Auth and Keplr work to secure vulnerable social-login wallets.
The trouble began Friday, Nov. 6, when Web3Auth disclosed a security issue affecting infrastructure used by third-party services. By early Saturday, Keplr was reporting unauthorized transactions involving accounts created through Google and Apple authentication, prompting the wallet provider to disable both login methods.
Josh Lee, co-founder of Chainapsis, the company behind Keplr, subsequently clarified that the vulnerability originated with Web3Auth rather than Keplr’s own software. Early estimates suggested approximately 20% of social-login accounts were affected, although only a fraction had reportedly been exploited.
The distinction matters because Keplr’s social-login feature relies on third-party key infrastructure rather than conventional user-controlled recovery phrases. That convenience simplifies cryptocurrency onboarding but creates dependencies absent from traditional hardware-wallet and seed-phrase arrangements.
Blockchain analytics company Bitquery examined transactions spanning Nov. 6-7, identifying extensive wallet-draining activity across Cosmos Hub, Osmosis, Celestia, Akash, Noble, Dydx, Babylon, and Injective.
Its investigation estimated that collector addresses received assets worth at least $6.01 million, based on valuations recorded Nov. 7. Cosmos Hub represented approximately $3.50 million, followed by Osmosis at $1.04 million and Injective at $615,000.
Bitquery’s analysis counted approximately 44,700 distinct private keys involved in the activity, with 86% of affected wallets on seven linked networks experiencing transfers after Keplr’s initial warning. Median wallet losses were just $1.34, although the largest individual transfer approached $325,000.
Investigators also documented approximately 1.96 million staked ATOM moving without the customary 21-day unbonding period. The transactions employed liquid staking mechanisms, converting positions into transferable share tokens while redirecting roughly $251,000 in staking rewards.
Yet subsequent disclosures introduced an important complication. Keplr and Web3Auth confirmed that white-hat recovery operations were using the exposed access path to move vulnerable assets into protective custody.
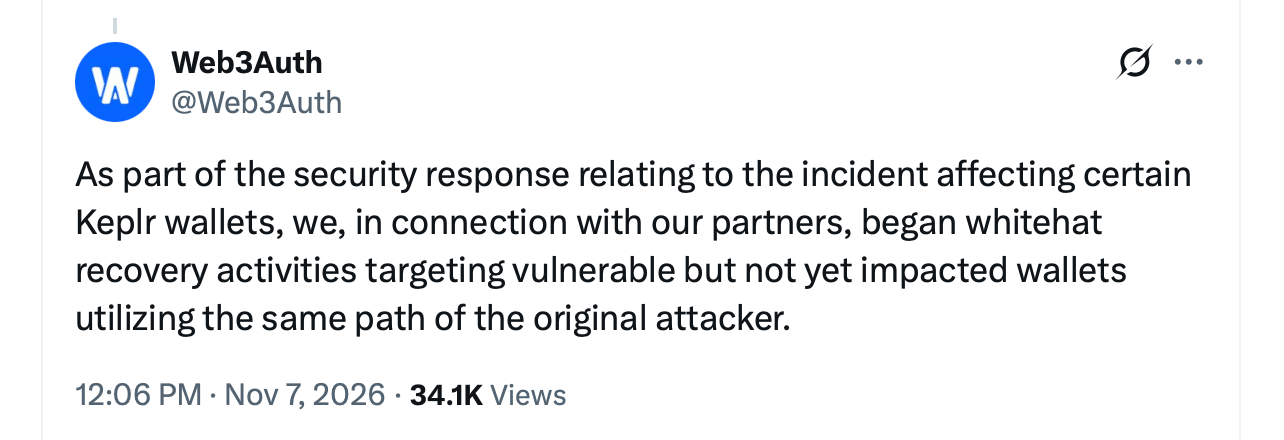
On Sunday, Nov. 8, Keplr identified recovery addresses that overlapped with several collector wallets examined by Bitquery. Consequently, the $6.01 million represents observed transfers, not a verified accounting of irrecoverable theft.
| Blockchain Network | Verified Recovery Address |
|---|---|
| Cosmos Hub | cosmos1atuap9kfnt6y8ykvn3437e7j3z8qffh3qtnmwu |
| Osmosis | osmo1atuap9kfnt6y8ykvn3437e7j3z8qffh3gsqtcw |
| Celestia | celestia1atuap9kfnt6y8ykvn3437e7j3z8qffh33pzt53 |
| Akash | akash1atuap9kfnt6y8ykvn3437e7j3z8qffh3ds7uhx |
| Noble | noble1atuap9kfnt6y8ykvn3437e7j3z8qffh3ggxnkj |
| Injective | inj1lqmdmuczn5rxn5jkc34wwrqdeh70etpf5wvt7g |
| dYdX | dydx1atuap9kfnt6y8ykvn3437e7j3z8qffh3fjalwt |
| Babylon | bbn1atuap9kfnt6y8ykvn3437e7j3z8qffh3h4z239 |
| Axelar | axelar1atuap9kfnt6y8ykvn3437e7j3z8qffh3y99n9a |
| Saga | saga1atuap9kfnt6y8ykvn3437e7j3z8qffh37c2ff6 |
| Agoric | agoric1atuap9kfnt6y8ykvn3437e7j3z8qffh3jk3y72 |
| EVM | 0x413e4F4De7E5FF010913488F781E679e76f706dA |
Source: Keplr and Web3Auth, Nov. 8, 2026. Addresses identified as associated with authorized recovery operations rather than malicious exploitation.
Web3Auth maintains that funds transferred through its protective operations remain secure. Keplr, meanwhile, cautioned that some affected users might encounter unexpectedly empty balances because their assets had been relocated for safekeeping.
The companies have not disclosed the vulnerability’s precise technical cause, established a definitive loss figure or announced a comprehensive reimbursement schedule.
Users who created accounts through the global technology companies Google or Apple should avoid depositing additional assets, transfer remaining liquid holdings into newly secured wallets and disregard unsolicited recovery offers. Staked assets may require additional processing.
For now, the incident exposes an uncomfortable contradiction in cryptocurrency wallet design. Simplifying private-key management can make blockchain applications more accessible, but outsourcing authentication introduces another potential point of failure. Until protective transfers are reconciled with malicious withdrawals, the industry’s latest multimillion-dollar security scare remains as much an accounting mystery as a technical emergency.
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到[email protected],本平台相关工作人员将会进行核查。


