Fake HR, fake CEO, plus an interview assignment containing malicious code, directly took away 6.3 billion dollars! 🧐
This Binance retrospective report is truly recommended for all developers and project teams working in Web3 to read carefully from start to finish.
To be honest, this level of security incident is definitely catastrophic. But let's see how Binance handled it afterwards, without whitewashing, shifting blame, or hiding things. The intrusion path, code details, operation logs, all made public. To be honest, this level of honesty is quite rare in exchanges!
Let me mention a few points that impressed me:
• 6.3 billion dollars stolen, Binance fully covered, users lost not a single cent.
• Only 3 days after the attack (as of October 31), 98% of the affected tokens were replenished, and the proof of reserves page is always available for verification.
• The timeline is very detailed, from October 30, 04:05 to 08:10, how the attacker used the new Ethereum feature EIP-7702, how they circumvented the MPC wallet's revocation logic, how they modified the local environment with scripts, all written out.
• Even the embarrassing fact that internal AI tools were misused as a springboard was admitted directly, and a third-party independent security company was invited for a secondary review.
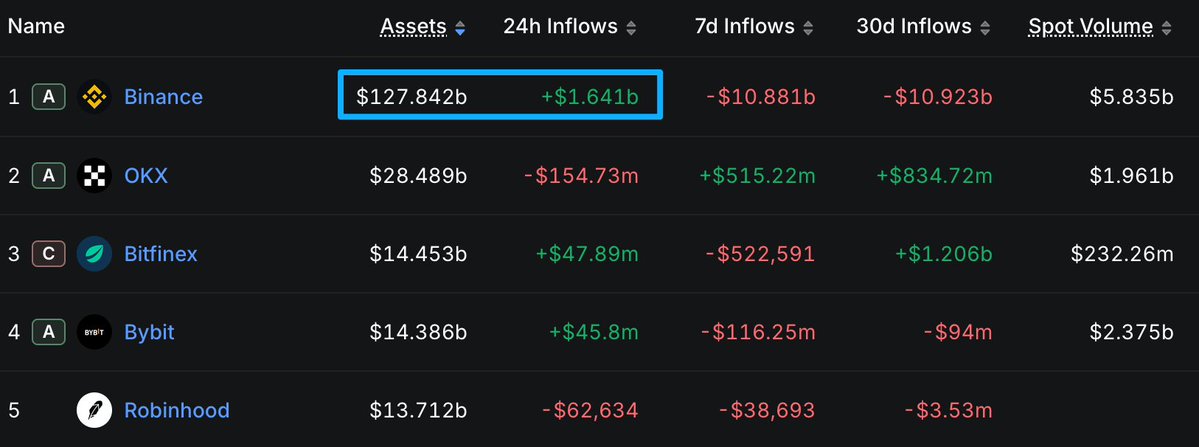
In the past, when exchanges had incidents, 9 out of 10 were vague. Binance's willingness to publish all the details this time shows a sincere attitude, and the system must have implemented higher-level protective measures. According to the latest 24-hour reserve data, there has already been a net inflow of up to 1.6 billion dollars (as shown in the image below), which is the most direct reflection!
When one door closes, another opens, this is like using 6.3 billion dollars as tuition to write a pitfall avoidance guide for the entire Web3 industry. Although the price is a bit high, it is worth serious study.
1️⃣ The source of tools must be clean. Install Homebrew, Python environments, etc., only from official channels, regularly verify hash values, and do not download modified versions haphazardly from search engines.
2️⃣ Do not run interview assignments on work computers. Any code sent from external sources, especially so-called test questions in job applications, must be isolated in a sandbox first; otherwise, it is like joking with the company wallet.
3️⃣ AI permissions should be tightened. With the increasing use of AI internally, permissions must be minimized, so it does not become a bridge for hackers to penetrate laterally.
Overall, Binance's decision to open the wound for the industry to see requires courage. While Binance indeed stumbled in defense, I think their accountability is commendable!
I hope this lesson can help Binance build a stronger security wall and issue a warning to the entire Web3 industry. After all, in the industry we are involved in, everyone hopes for lasting prosperity! 🙏 @binancezh @moonkimbinance
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到[email protected],本平台相关工作人员将会进行核查。


