If even hardware wallets may be tampered with during circulation, can offline storage of private keys ensure asset safety?
In mid-October, the Ledger hardware wallet supply chain incident sparked concern. According to multiple media reports, attackers purchased legitimate devices, opened the casing, implanted hidden components capable of reading user recovery phrases, and then resold them through Southeast Asian distribution channels. On-chain investigations estimate that the related incidents may have caused losses of over 86 million dollars in cryptocurrency assets, but the exact scale of losses has yet to be fully confirmed by Ledger.
Ledger stated that it has confirmed the existence of unauthorized hardware implants in affected devices and pointed out that the currently confirmed cases involve specific distribution channels, rather than breaches in its core chips, operating systems, or servers.
This incident exposes risks that are not traditional smart contract vulnerabilities, but rather the potential for devices to be tampered with during transportation, sales, and resale after leaving the manufacturer's control.
Security concerns are expanding from "Are there vulnerabilities in the code?" to "What has the device gone through before it reaches the user?"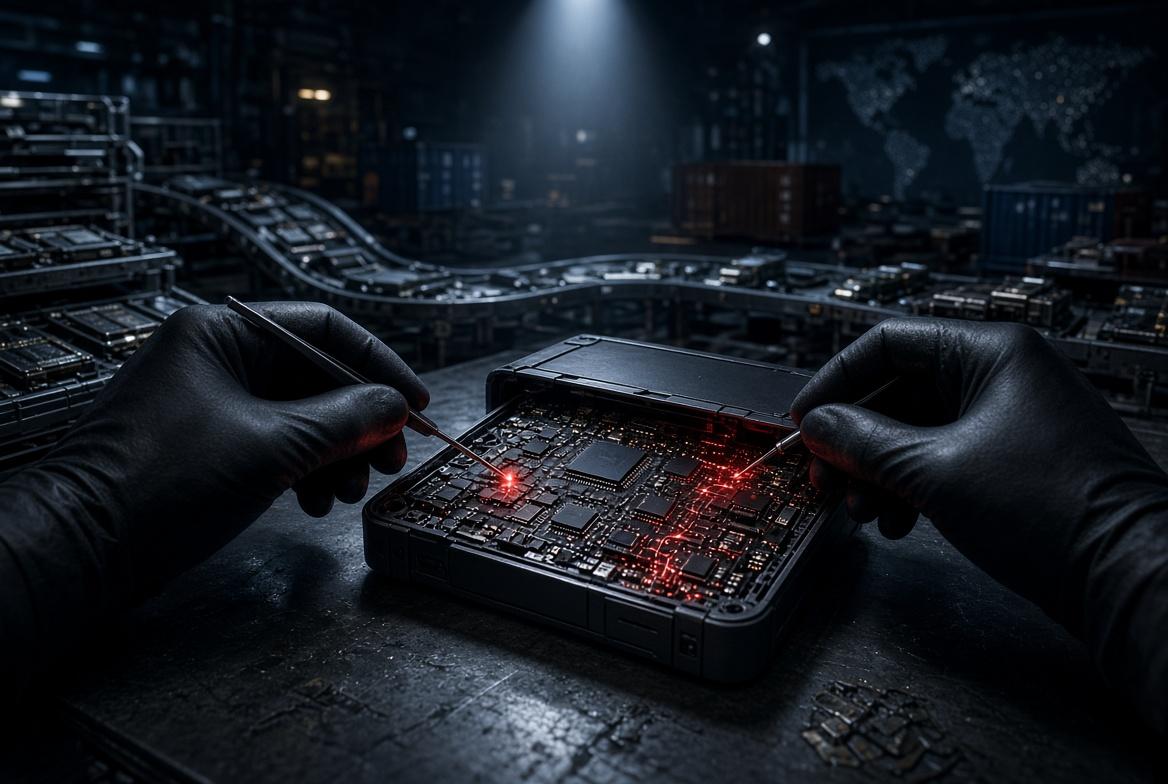
From auditing code to inspecting the entire supply chain
In the past, conversations about cryptocurrency security typically focused on smart contract audits, private key management, and transaction signatures. However, the security of hardware wallets depends not only on the chips and software but also on whether devices are delivered through authorized channels, whether they have been tampered with, and whether users can detect anomalies.
Even if the device uses secure chips, if attackers are able to implant additional hardware during the circulation phase to steal recovery phrases, the original advantage of offline storage may be undermined.
Ledger has stated that it will strengthen dealer management, remind authorized channels not to resell returned devices, and adjust product display and inventory management methods. The company’s new device, Atom, also incorporates measures such as casing opening detection, tamper-proof design, and anti-tampering packaging, and plans to sell exclusively through its official website.
These changes reflect a shift in hardware security, moving from reliance on a single secure element to simultaneously focusing on device structure, integrity checks, and sales channels.
Tamper-proofing is becoming part of product competition
For hardware wallet manufacturers, security is no longer just about promoting chip levels or audit reports. Whether the device can detect if the casing has been opened, if key components have been interfered with, if the packaging shows signs of being unsealed, and whether abnormal devices can be traced in a timely manner, may all become key factors in users' product choices.
Protection on the user side is equally important. When purchasing devices, prioritize official channels; upon receiving the device, check for any abnormalities in the packaging and casing, and strictly follow the manufacturer's initialization process. Recovery phrases should not be entered into webpages or applications of unknown origin, nor should they be given to customer service or anyone claiming to assist in asset recovery.
If tampering is suspected, cease use immediately and verify through the manufacturer's official channels. For already exposed recovery phrases, simply replacing the device is not sufficient; a new wallet must be created in a trusted environment, and assets should be transferred to the new wallet.
The boundaries of self-custody need to be redefined
Self-custody allows users to maintain control of their assets, but it also means users must shoulder responsibilities such as device procurement, recovery phrase storage, and transaction verification. Institutional custody can provide professional security management and process control, but still needs to address internal permissions, third-party services, and operational risks.
There is no absolute answer to safety for either model; the key lies in who bears the risks and whether corresponding protective mechanisms are established.
For the entire industry, the lessons from this incident are: security cannot merely be a one-time audit completed before product release, but should permeate the entire lifecycle of device manufacturing, distribution, use, and asset management.
As attackers begin to bypass code and directly seek weaknesses in hardware and supply chains, genuinely competitive security products must demonstrate that they can not only defend against hackers but also detect if devices have been tampered with.
If you are also paying attention to the crypto market and want to participate in trading or asset allocation, you can register through the following exclusive channels to enjoy discounts:
Binance: Register through the exclusive link and fill in the invitation code aicoin668 to enjoy a 10% rebate.
Registration Link: https://jump.do/zh-Hans/xlink-proxy?id=3
Benefits Group: https://www.aicoin.com/link/chat?cid=gmLgwvKD1
OKX: Register through the AiCoin exclusive link and enjoy a permanent 20% rebate.
Registration Link: https://jump.do/zh-Hans/xlink-proxy?id=2
Benefits Group: https://aicoin.com/link/chat?cid=l61eM4owQ
Bitget: Register through AiCoin's exclusive channel to enjoy a 10% transaction fee rebate.
Registration Link: https://jump.do/zh-Hans/xlink-proxy?id=6
Benefits Group: https://aicoin.com/link/chat?cid=N63yYYKQE
You are also welcome to join the AiCoin-related community to get more information on new coins and earning opportunities:
Official Telegram Community: https://t.me/aicoin_support
AiCoin Chinese Twitter: https://x.com/AiCoinzh
This content represents the author's personal views and does not represent the position of this platform. The opinions, conclusions, and suggestions in the article are for investors' reference only and do not constitute any investment advice related to this platform. The market has risks; investment must be cautious.
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到[email protected],本平台相关工作人员将会进行核查。